A plain-English guide to UK GDPR: what it is, who it applies to, the principles and rights it protects, and what changed under the 2025 Data (Use and Access) Act.
UK GDPR governs how organisations handle personal information. This guide explains the main requirements and the amendments made by the Data (Use and Access) Act 2025. The Act's data protection and PECR provisions were in force by 19 June 2026.
Processing information about staff, customers or other identifiable people will commonly bring an organisation within UK GDPR. Its territorial scope and any specific exemptions still need checking. This page explains the main rules and links to detailed guides.
GDPR in one sentence
GDPR is a regulation that sets out how organisations must handle the personal information of identifiable people. Its purpose is to give individuals meaningful control over how their data is collected, used, shared, and stored, and to hold the organisations using that data to a documented standard of care.
UK GDPR covers a wide range of organisational processing, subject to its material and territorial scope. The Information Commission, which continues to use the ICO name after its 30 September 2026 transition, regulates compliance through guidance, investigations, notices, reprimands and fines.
What does GDPR stand for?
GDPR stands for General Data Protection Regulation. It was originally an EU regulation, adopted in April 2016 and enforceable across the European Union — including the United Kingdom — from 25 May 2018.
After Brexit, the UK adopted its own version, known formally as the UK GDPR, which sits alongside the Data Protection Act 2018. The two are sometimes described as a single regime: the UK GDPR provides the main rules, the Data Protection Act 2018 fills in UK-specific detail.
When did GDPR come into force?
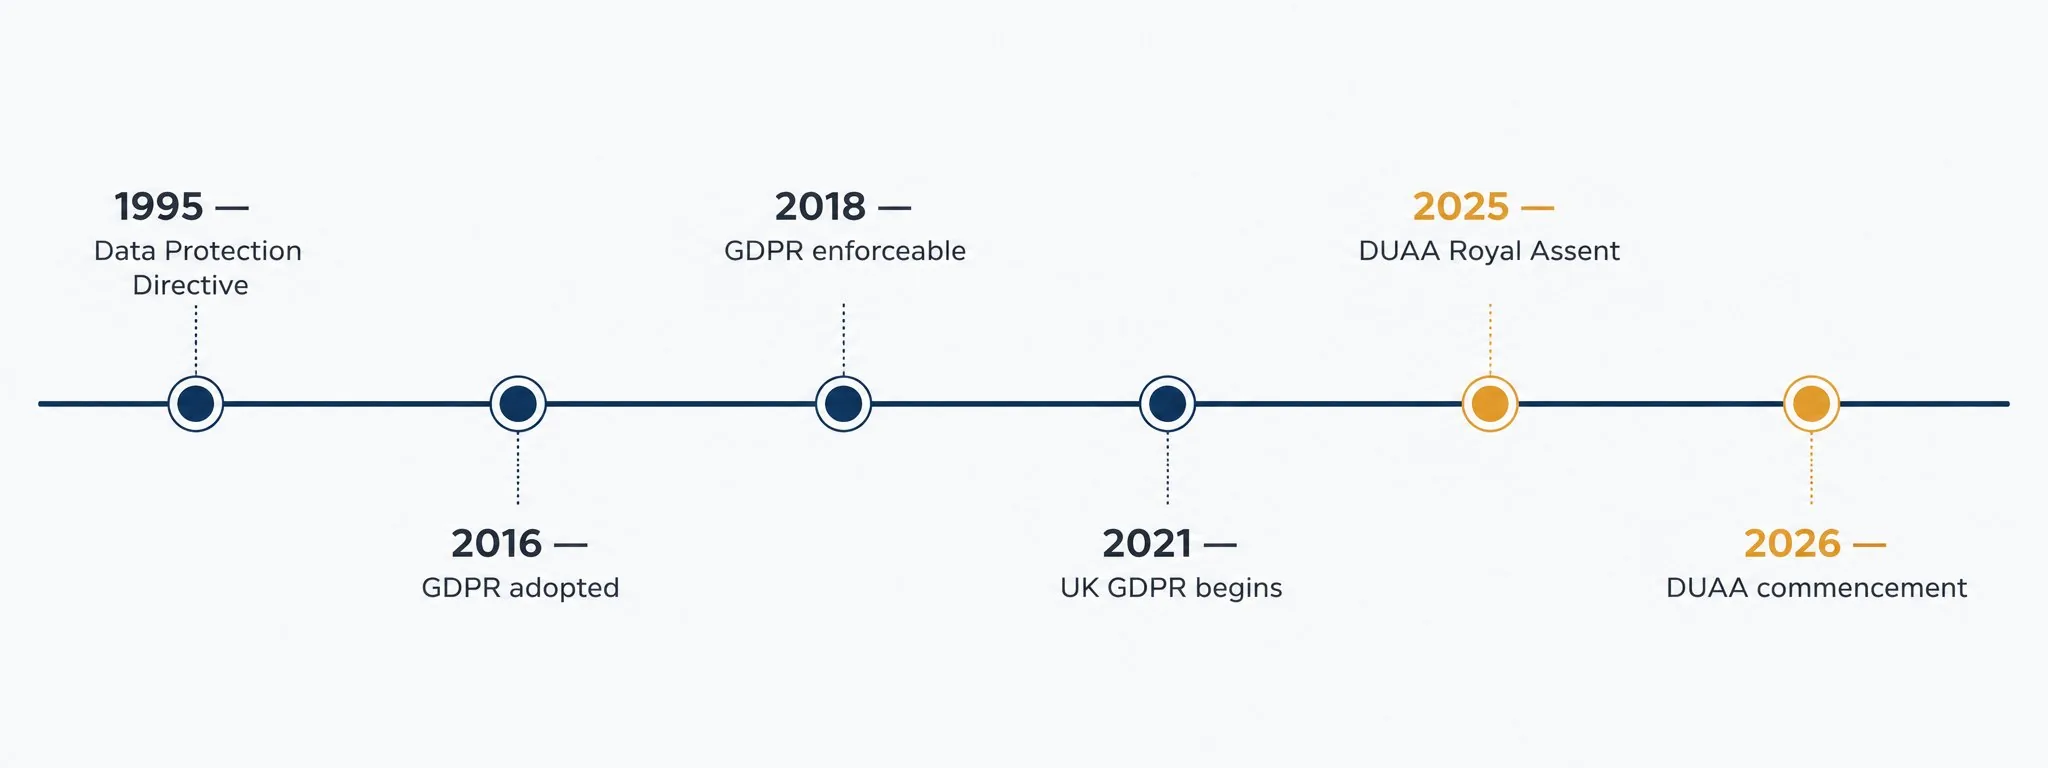
The EU GDPR was adopted by the European Parliament on 14 April 2016. It then went through a two-year transition period before becoming directly enforceable on 25 May 2018. On the same day, the UK’s Data Protection Act 2018 came into effect, replacing the older Data Protection Act 1998.
When the Brexit transition period ended on 31 December 2020, the EU GDPR stopped applying directly to the UK. From 1 January 2021, the UK has had its own version: the UK GDPR. It is substantively similar to the EU regulation, but the two have begun to diverge — particularly since the Data (Use and Access) Act 2025 introduced UK-specific reforms.
The DUAA received Royal Assent on 19 June 2025. A major group of changes commenced on 5 February 2026, and the new organisational complaints procedure requirement took effect on 19 June 2026.
For a fuller breakdown of dates and what each one means, see our GDPR history and timeline guide.
Who does GDPR apply to?
UK GDPR applies to organisations established in the UK that process personal data, regardless of where the processing itself happens. It also applies to organisations outside the UK that offer goods or services to people in the UK, or that monitor the behaviour of people in the UK (for example, by tracking visitors to a UK-targeted website).
There is no general exemption for small businesses, charities, or sole traders. If you collect customer emails, run a payroll, manage a membership list, or operate a CCTV camera that captures the street outside your premises, GDPR is in scope. The small-business friendly bits of the regulation are mostly about proportionality — what the rules require of you can scale with the risk you create — not about exemptions from the rules themselves.
A narrow “household exemption” carves out purely personal or domestic activity from the regulation. A homeowner’s CCTV system that records only their own driveway sits within the exemption. The moment that camera captures the neighbour’s garden or a public footpath, the exemption falls away — as the Oxford County Court confirmed in Fairhurst v Woodard in 2021.
Our scope guide covers the territorial reach, the household exemption, and what GDPR means for charities, sole traders, and small businesses specifically.
UK GDPR vs EU GDPR
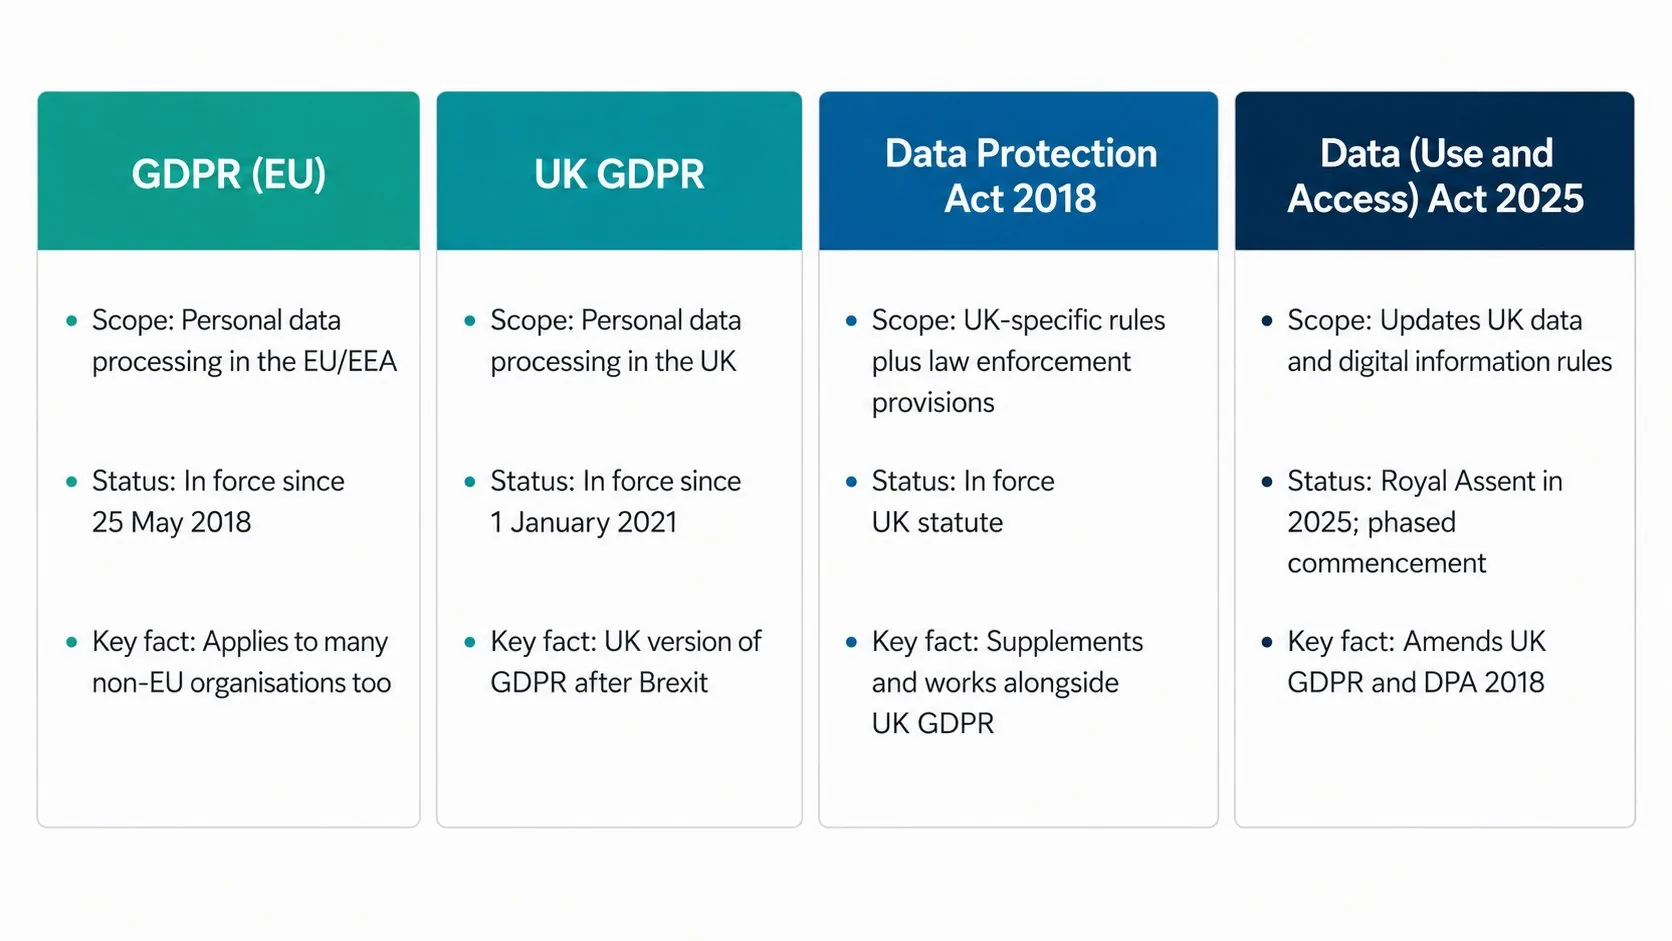
For most of the period from 2021 to 2024, the UK GDPR and the EU GDPR were practically identical. That has changed.
The Data (Use and Access) Act 2025 introduced a new lawful basis (“recognised legitimate interests”) that does not exist in the EU regulation. It replaced Article 22 of the UK GDPR (the automated decision-making rule) with new Articles 22A to 22D, which give organisations more flexibility. It expanded the list of cookies and similar technologies that no longer require consent under PECR. And it changed the test that applies to international data transfers from the EU’s “essential equivalence” standard to a UK-specific “not materially lower” test.
None of this means UK and EU GDPR have become wholly different regimes. They share the same principles, the same definitions of personal data, the same controller/processor framework, and most of the same individual rights. But the divergence is real, and on a path that is likely to continue.
The European Commission renewed the UK’s adequacy decision on 19 December 2025, extending it until 27 December 2031. That means, for now, personal data can continue to flow freely from the EU to the UK without additional safeguards.
For the full comparison see our UK GDPR vs EU GDPR guide.
The 7 principles of GDPR
Article 5 of the UK GDPR sets out seven principles that underpin everything else in the regulation. Six of them are listed in Article 5(1); the seventh — accountability — sits in Article 5(2) and applies on top of the others.
The principles are:
- Lawfulness, fairness and transparency. You need a lawful basis for processing, you must treat people fairly, and you must be open about what you are doing.
- Purpose limitation. Define the original purposes and check whether a new use is compatible under the applicable rules. You must also identify a lawful basis; choosing a different basis does not automatically make an incompatible use lawful.
- Data minimisation. Collect what you need for the stated purpose. Nothing more.
- Accuracy. Keep personal data accurate and up to date. Correct or delete inaccurate data without delay.
- Storage limitation. Don’t keep personal data for longer than you need it.
- Integrity and confidentiality (security). Protect personal data against loss, theft, and unauthorised access.
- Accountability. Be able to demonstrate that you comply with all of the above.
These are not aspirations or best practices. They are legal obligations, and the burden of proving compliance sits with the organisation. The accountability principle in particular is what makes GDPR a documented compliance regime rather than a trust-based one.
For per-principle detail see our seven principles of GDPR guide.
Rights of individuals
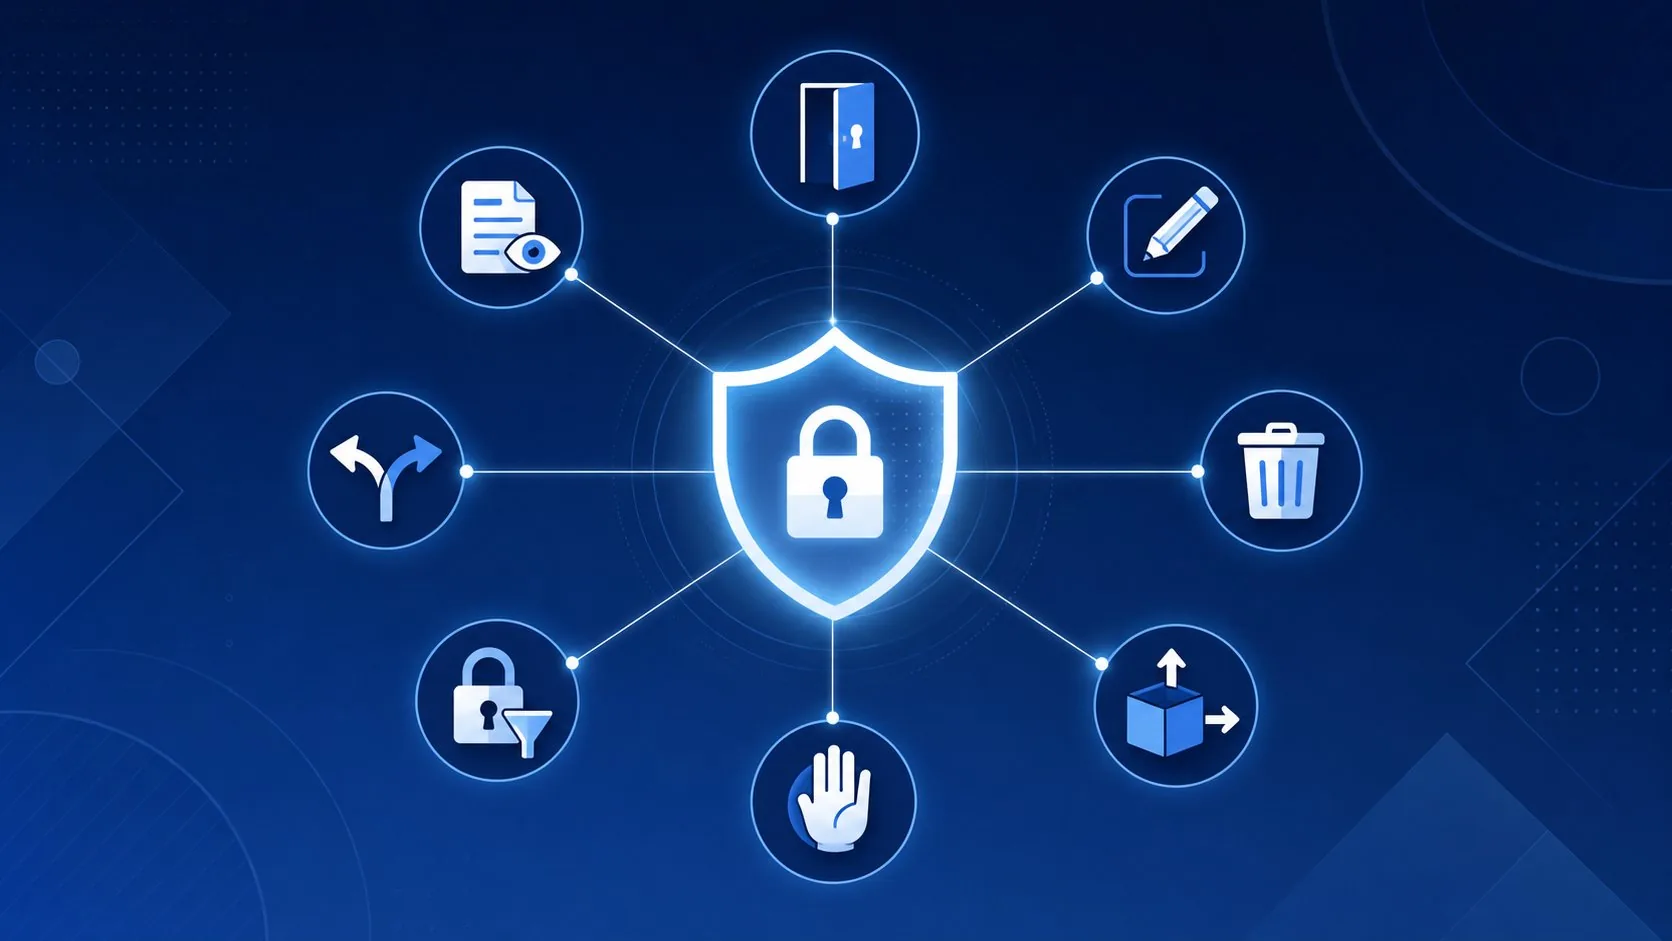
GDPR gives individuals (called “data subjects” in the regulation) eight specific rights over their personal data:
- The right to be informed — to know what data is being collected, by whom, for what purpose, and for how long.
- The right of access — to obtain a copy of the personal data an organisation holds about them. Requests are known as Subject Access Requests, or SARs.
- The right to rectification — to have inaccurate data corrected.
- The right to erasure (often called the “right to be forgotten”) — to have data deleted in certain circumstances.
- The right to restrict processing — to limit how their data is used.
- The right to data portability — to receive their data in a portable format and to send it to another provider.
- The right to object — including an absolute right to opt out of direct marketing.
- Rights related to automated decision-making and profiling — including the right to human intervention in significant automated decisions. These rules were substantially rewritten by the DUAA.
Individuals can normally exercise their rights without a fee. Many requests must be answered without undue delay and within one calendar month, with a permitted extension for complexity or the number of requests. Timing rules can also address necessary identity checks and clarification of access requests. Since 19 June 2026, controllers must facilitate data protection complaints, acknowledge them within 30 days and take appropriate steps to respond without undue delay.
Our data subject rights guide covers each right in detail, including how to handle a Subject Access Request.
Key roles: controller and processor
GDPR distinguishes between two main roles. A controller is the organisation that decides why and how personal data is processed. A processor is an organisation that processes personal data on the controller’s instructions.
If you run a customer database, you are the controller. If you use an email marketing platform to send messages to that database, the platform is acting as your processor. If a school records its pupils’ attendance using a third-party software supplier, the school is the controller and the supplier is the processor.
The two roles carry different obligations. Controllers must identify a lawful basis for processing, respond to subject access requests, conduct impact assessments where appropriate, and maintain records of their processing activities. Processors must follow the controller’s instructions, keep their own records, implement appropriate security, and notify the controller of any breach.
Processing by a processor must be governed by a binding written contract or other legal act meeting Article 28's requirements.
Some organisations are controllers for some processing and processors for other processing. The classification depends on the specific activity, not the organisation as a whole. Our controller vs processor guide walks through how to determine which role you are in each case.
What counts as personal data?
Personal data is any information that relates to an identified or identifiable living person. A name, address, or phone number is obviously personal data. So is an email address, an IP address logged in a server, a customer reference number, a CCTV image, a voice recording, and in many contexts a vehicle registration plate.
The test is whether the person can be identified — directly, or indirectly when the data is combined with other information. An anonymous customer ID on its own may not be personal data, but the same ID held alongside a separate file that links it to a name becomes personal data in both files.
A subset of personal data, called special category data, gets extra protection under Article 9. This includes data revealing racial or ethnic origin, political opinions, religious beliefs, trade union membership, genetic data, biometric data used for identification, health information, and information about sex life or sexual orientation. Processing special category data requires both a lawful basis and a separate Article 9 condition.
UK GDPR protects identifiable living individuals. It does not cover information solely about deceased people or companies. Anonymised information falls outside it when identification is not reasonably likely, considering available means and context. Replacing names with reversible codes normally produces pseudonymised personal data, which remains protected.
For the full definition and edge cases, see our personal data guide.
Penalties for non-compliance
The standard UK GDPR maximum is £8.7 million or 2% of the undertaking's total worldwide annual turnover, whichever is higher. The higher maximum is £17.5 million or 4%, whichever is higher. The applicable tier depends on the provision infringed; the ICO assesses the circumstances when deciding whether to fine and how much.
The ICO's 2025/26 annual report records eight UK GDPR penalty notices totalling £32,402,373, compared with two totalling £3,826,320 in 2024/25. These financial-year figures should not be mixed with calendar-year totals or PECR penalties.
An intention to fine is not a final penalty. For example, the ICO announced a proposed British Airways penalty in 2019 before issuing its final £20 million penalty in October 2020. The change was part of the regulatory decision process, not a reduction of an already-issued fine on appeal.
Fines are not the only enforcement tool. The ICO can issue enforcement notices requiring specific action, public reprimands, and audits. Individuals can also bring civil compensation claims under Article 82.
The DUAA raised the higher PECR penalty maximum to £17.5 million or 4% of an undertaking’s worldwide annual turnover, whichever is higher, from 5 February 2026. The fixed sterling cap is 35 times its former £500,000 amount; this does not mean individual penalties automatically increase by that multiple.
For the full enforcement picture, including how the ICO calculates fines, see our GDPR fines guide.
What’s changed under the DUAA 2025
The Data (Use and Access) Act 2025 is the most significant change to UK data protection law since 2018. It does not replace UK GDPR, the Data Protection Act 2018, or PECR — but it amends all three. The key reforms that affect day-to-day compliance:
- Recognised legitimate interest is a seventh lawful basis for specified purposes such as safeguarding, emergencies and crime prevention. Its conditions and a necessity test still apply, but there is no separate balancing test. Standard legitimate interests normally require that balancing assessment.
- Articles 22A–22D allow significant solely automated decisions in a wider range of situations, with safeguards including information, representations, human intervention and a route to contest the decision. Recognised legitimate interest cannot be used for these decisions. Special category data remains subject to additional restrictions.
- A new direct right to complain — data subjects can now lodge complaints directly with controllers, who must acknowledge them within 30 days. This is in addition to the existing right to complain to the ICO.
- PECR now has five consent exceptions in total: communication, strictly necessary, statistical purposes, appearance and emergency assistance. The DUAA added the last three; it did not create five new exceptions. Their conditions must be met, including clear information and a simple free objection mechanism for the statistical and appearance exceptions.
- Scientific research provisions allow qualifying broad consent and, in specified circumstances, an exception from providing additional privacy information where this is impossible or disproportionate. The relevant conditions and safeguards still apply; research is not generally exempt from transparency.
- Children’s online services — explicit requirements for online services likely to be used by children to take account of “children’s higher protection matters” when designing those services.
- The regulator formally became the Information Commission on 30 September 2026, replacing the single-Commissioner model with collective board governance. It continues to use the ICO name.
Implementation was phased. By 19 June 2026, all the Act's data protection and PECR provisions were in force. Separate institutional changes to the regulator should not be confused with commencement of organisations' duties.
Where to go next
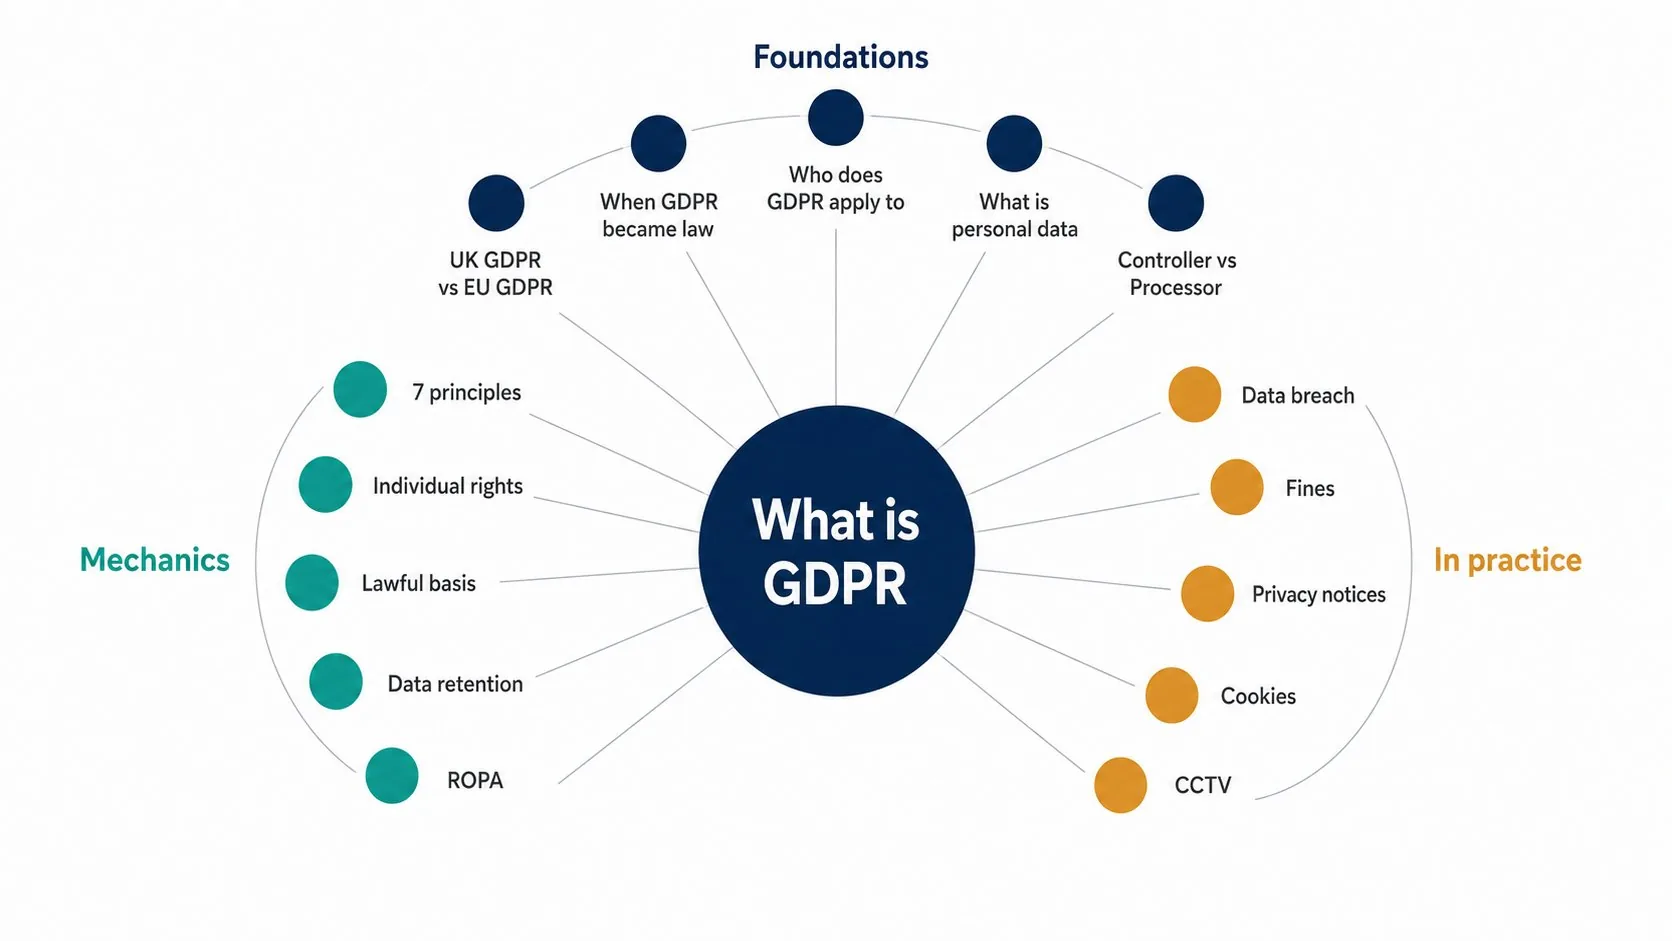
This guide covers the essentials. For depth on each subtopic, follow the links below:
Foundations
- When did GDPR become law?
- Who does GDPR apply to in the UK?
- UK GDPR vs EU GDPR
- What is personal data under GDPR?
- Data controller vs data processor
Mechanics
- The 7 principles of GDPR
- Individual rights under GDPR
- GDPR lawful basis and consent
- GDPR data retention periods
- GDPR ROPA and Article 30
In practice
- GDPR data breach: what to do
- GDPR fines and penalties
- GDPR privacy notices explained
- GDPR cookie consent in the UK
- GDPR and CCTV in the UK
Reading is a good start. If your team needs to actually do GDPR compliance — set up the right processes, handle requests properly, train staff to spot the issues that lead to fines — that’s a different problem from understanding what the law says. Our GDPR & Data Protection Course covers both: the regulation as it stands today, and the practical compliance habits that keep organisations out of trouble.
Frequently asked questions
Is GDPR still in force after Brexit?
Yes. The UK adopted its own version of the regulation, known as UK GDPR, which has applied since 1 January 2021. It sits alongside the Data Protection Act 2018.
What’s the difference between UK GDPR and the Data Protection Act 2018?
UK GDPR provides the core rules; the Data Protection Act 2018 supplements it with UK-specific detail (for example, around law enforcement processing, children’s data, and exemptions). They are two separate pieces of legislation that work together. UK GDPR is not a different name for the Data Protection Act, despite what some online guides suggest.
Does GDPR apply to small businesses?
There is no general small-business exemption. Some duties have specific thresholds or exceptions: Article 30 permits a limited exemption for certain occasional, low-risk processing by organisations with fewer than 250 employees, but not for their regular, risky, special category or criminal offence data processing.
What’s changing under the DUAA in 2026?
The DUAA introduced a seventh lawful basis, amended significant automated decisions, added cookie exceptions and introduced controller complaints duties. Its data protection and PECR provisions are now in force. The regulator transitioned to the Information Commission on 30 September 2026.
Who enforces GDPR in the UK?
The Information Commission, known publicly as the ICO. Its 30 September 2026 governance transition preserved its core regulatory work, including complaints, guidance, investigations, audits and enforcement.
When did GDPR become law?
GDPR was adopted by the EU on 14 April 2016 and became enforceable on 25 May 2018. UK GDPR has applied since 1 January 2021.
What is personal data?
Any information that relates to an identifiable living person — including names, contact details, IP addresses, photos, online identifiers, and more.
What happens if you breach GDPR?
The ICO can issue fines of up to £17.5 million or 4% of global turnover, alongside other enforcement actions like reprimands, audits, and enforcement notices. Affected individuals can also bring civil compensation claims.
Related guides
- GDPR cookie consent in the UK: rules after the DUAA 2025
- GDPR fines and penalties in the UK: how big, who pays, what counts
- GDPR data breach: what to do in the first 72 hours
Make sure your team can actually do GDPR compliance — not just read about it.
Explore the GDPR & Data Protection Course →Sources & references
- UK GDPR: current legislation
- ICO: Data (Use and Access) Act 2025 commencement and guidance
- ICO: automated decisions, recognised legitimate interest and other DUAA changes
- ICO: the five storage and access exceptions
- ICO: handling data protection complaints
- ICO: Annual Report 2025/26
- ICO: transition to the Information Commission
- ICO: EEA-to-UK adequacy until 27 December 2031
Mark writes about data protection, GDPR compliance and accredited online training for GDPR & Data Protection Course, part of Online CPD Academy.