The European Parliament approved GDPR on 14 April 2016. The regulation is dated 27 April 2016, entered into force on 24 May 2016 and began applying on 25 May 2018. This guide distinguishes those dates and later UK changes.
The short answer most people are looking for: GDPR became enforceable across the EU, including the UK, on 25 May 2018. But that date is only one of several that matter. There are at least four that an organisation needs to know — the adoption date, the enforcement date, the post-Brexit transition, and the more recent reforms under the Data (Use and Access) Act 2025.
This guide covers each in order, with the context that explains why each one matters.
Why GDPR was created
Before GDPR, EU data protection law was based on the Data Protection Directive 95/46/EC, which the UK had implemented through the Data Protection Act 1998. The directive predated smartphones, social media, mass cloud computing, and the data-driven economy. It also produced patchy enforcement across EU member states, because each country implemented it through its own national law.
GDPR was designed to replace that fragmented system with a single, directly applicable regulation across the EU. The European Commission proposed it in 2012, the European Parliament and Council adopted it in 2016, and it became enforceable in 2018 — by which point the technologies and business models it was designed to regulate were unrecognisable from the 1995 baseline.
The DPA 1998 was repealed and replaced by the Data Protection Act 2018 on the same day GDPR became enforceable.
Parliament approved GDPR on 14 April 2016
The European Parliament approved the Council's position on 14 April 2016. The final Regulation(EU)2016/679 is dated 27 April 2016, was published on 4 May 2016 and entered into force on 24 May 2016. It began applying two years later, on 25 May 2018.
Entry into force and the date of application are different. GDPR entered into force on 24 May 2016, while Article 99 set 25 May 2018 as the date from which its substantive rules applied. Organisations had the intervening period to prepare.
GDPR became enforceable on 25 May 2018
The “go live” date — the one most people mean when they ask when GDPR became law — is 25 May 2018. From that day, organisations subject to GDPR could be fined, audited, and sanctioned for non-compliance.
The same date marked another important UK change: the Data Protection Act 2018 came into effect, replacing the Data Protection Act 1998. The DPA 2018 had received Royal Assent two days earlier, on 23 May 2018. Its purpose was to supplement GDPR with UK-specific provisions — covering law enforcement processing, intelligence services, and a long list of exemptions — and to align the broader UK data protection framework with the new EU rules.
For UK organisations between May 2018 and the end of 2020, two parallel regimes applied: the EU GDPR directly, and the DPA 2018 alongside it. That arrangement ended with Brexit.
UK GDPR took effect on 1 January 2021
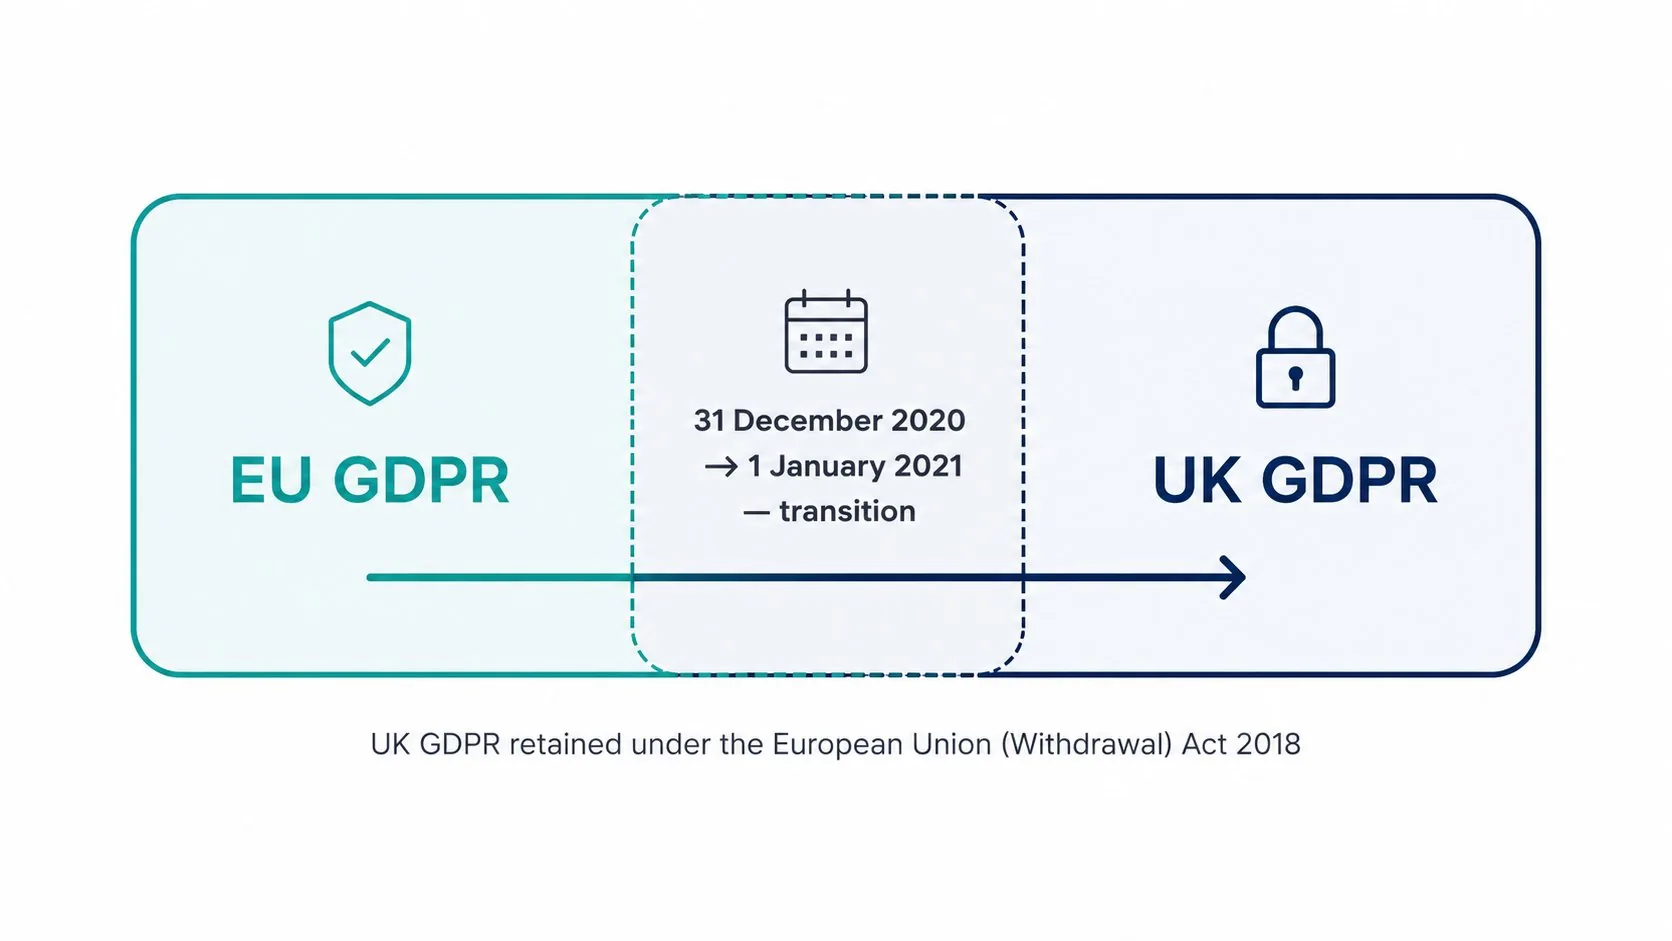
The UK formally left the European Union on 31 January 2020, but EU law continued to apply during a transition period that ended at 11pm on 31 December 2020. From 1 January 2021, EU GDPR stopped applying directly in the UK.
To prevent a gap in protection, the UK retained GDPR in domestic law under the European Union (Withdrawal) Act 2018. The retained version, with some technical amendments to fit a non-EU context, is known as UK GDPR. It applies to UK-based organisations and to overseas organisations targeting people in the UK.
For most practical purposes, the change between 31 December 2020 and 1 January 2021 was invisible. The principles, rights, lawful bases, and enforcement framework all carried over. What changed was the constitutional basis — the rules now sat in UK law, regulated by the ICO under UK jurisdiction, rather than in directly applicable EU law.
The European Commission confirmed an adequacy decision for the UK on 28 June 2021, allowing personal data to flow freely from the EU to the UK. That decision was renewed on 19 December 2025, extended until 27 December 2031.
The Data (Use and Access) Act 2025
The first significant change to UK GDPR since adoption came in 2025. The Data (Use and Access) Act 2025 received Royal Assent on 19 June 2025, after passing both Houses of Parliament earlier that month.
The DUAA amends UK GDPR, the Data Protection Act 2018, and PECR — it does not replace any of them. Its provisions came into force in phases:
- 19 June 2025 — the reasonable-and-proportionate search requirement for subject access requests took effect at Royal Assent.
- 5 February 2026 — the largest single batch of reforms came into force. This included the new lawful basis of “recognised legitimate interests”, the rewrite of Article 22 on automated decision-making, new exemptions for low-risk cookies under PECR, the alignment of PECR fines with UK GDPR, and changes to the test for international data transfers.
- April 2026 — the ICO finalised its updated Storage and Access Technologies guidance, replacing the older cookies guidance.
- 19 June 2026 — the new complaints requirements came into force, including acknowledgement within 30 days and a response without undue delay.
All DUAA provisions affecting data protection law and PECR are now in force. The regulator formally transitioned to the Information Commission on 30 September 2026 and continues to use the ICO name.
For more detail on what the DUAA actually changes, see our hub guide to UK GDPR and our UK GDPR vs EU GDPR guide.
Quick reference: the dates that matter
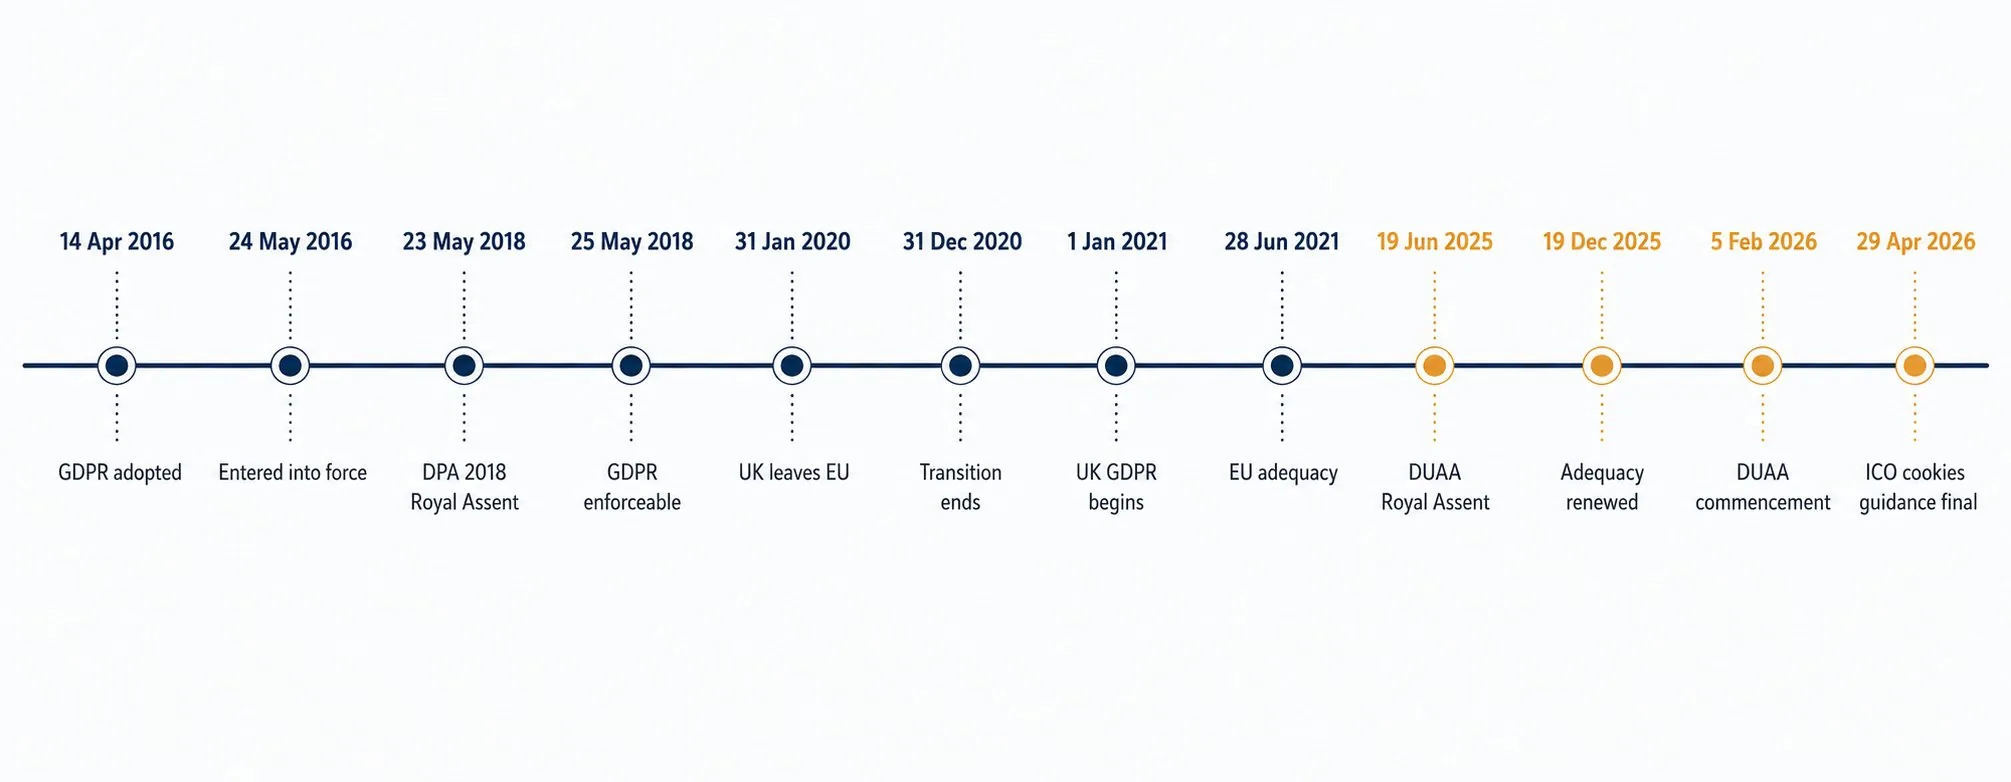
- 14 April 2016 — the European Parliament approves the Council's position; the final regulation is dated 27 April 2016.
- 24 May 2016 — GDPR entered into force; two-year transition begins.
- 23 May 2018 — UK Data Protection Act 2018 receives Royal Assent.
- 25 May 2018 — GDPR becomes enforceable across the EU, including the UK. DPA 2018 takes effect.
- 31 January 2020 — UK leaves the European Union.
- 31 December 2020 — Brexit transition period ends.
- 1 January 2021 — UK GDPR takes effect.
- 28 June 2021 — EU adequacy decision for the UK.
- 19 June 2025 — Data (Use and Access) Act 2025 receives Royal Assent.
- 19 December 2025 — EU adequacy decision renewed (valid until 27 December 2031).
- 5 February 2026 — main batch of DUAA provisions in force.
- 29 April 2026 — ICO Storage and Access Technologies guidance finalised.
- 19 June 2026 — controller complaints duties begin;30 September 2026 — the regulator transitions to the Information Commission.
Frequently asked questions
When did GDPR come into force?
GDPR entered into force on 24 May 2016, with a two-year transition period before it became enforceable on 25 May 2018.
When was GDPR introduced?
The Commission proposed GDPR in January 2012. Parliament approved it on 14 April 2016; the final regulation is dated 27 April 2016. It entered into force on 24 May 2016 and began applying on 25 May 2018.
What year did GDPR start?
GDPR began applying as enforceable law in 2018. In the UK, the retained UK GDPR has been in effect since 1 January 2021.
When did the UK adopt GDPR?
The UK was an EU member state when GDPR became enforceable on 25 May 2018, so it applied directly. After Brexit, the UK retained GDPR in domestic law, and UK GDPR took effect on 1 January 2021.
When does the DUAA take effect?
The DUAA received Royal Assent on 19 June 2025 and commenced in stages. Many core reforms took effect on 5 February 2026, complaints duties on 19 June 2026, and the regulator transition on 30 September 2026. Its data protection and PECR changes are now in force.
Related guides
- GDPR cookie consent in the UK: rules after the DUAA 2025
- GDPR data breach: what to do in the first 72 hours
- Individual rights under GDPR
Make sure your team understands UK data protection law and can handle personal data safely.
Explore the GDPR & Data Protection Course →Sources & references
- EU GDPR: publication and Article 99
- EUR-Lex: legislative history
- Data Protection Act 2018
- ICO: DUAA commencement
- ICO: transition on 30 September 2026
- European Commission: UK adequacy decisions
- ICO: SAR guidance, February 2026, page 6
Mark writes about data protection, GDPR compliance and accredited online training for GDPR & Data Protection Course, part of Online CPD Academy.