A clear guide to who must comply with UK GDPR — including UK and overseas organisations, charities, sole traders, the household exemption, and how the ICO enforces the rules.
GDPR applies to almost every UK organisation that handles information about people. The exceptions are narrow, the territorial reach is wide, and the size of the organisation is mostly irrelevant. If you have employees, customers, or website visitors, the regulation is in scope.
This guide covers who must comply, the territorial rules that pull in overseas organisations, the household exemption that protects strictly personal use, and the regulator's role in enforcing the rules.
The short answer
UK GDPR generally covers automated processing of personal data and manual information in, or intended for, a structured filing system, where its territorial rules apply. It excludes purely personal or household processing and certain other activities. Law enforcement and intelligence processing have separate Data Protection Act regimes.
In practice, that captures:
- All UK businesses, charities, partnerships, sole traders, and public bodies that handle personal data — which is nearly all of them.
- Overseas organisations that offer goods or services to people in the UK, or that monitor the behaviour of people in the UK.
The UK regulator formally became the Information Commission on 30 September 2026. Its public-facing name is the Information Commission's Office, or ICO.
Organisations established in the UK
Article 3(1) of the UK GDPR is the primary scope rule for domestic organisations. It applies to processing carried out in the context of the activities of an establishment in the UK, regardless of where the processing itself takes place.
"Establishment" is interpreted broadly. It includes registered companies, partnerships, LLPs, charities, sole traders trading under a business name, public bodies, and unincorporated associations. The processing might be carried out by a server in Ireland or a cloud provider in the United States — what matters is whether the processing is connected to the activities of a UK establishment.
There is no general small-business exemption. The duties applying to an activity depend on its nature, role and risk, with specific exceptions or thresholds for matters such as records and DPO appointment.
Organisations outside the UK selling into the UK
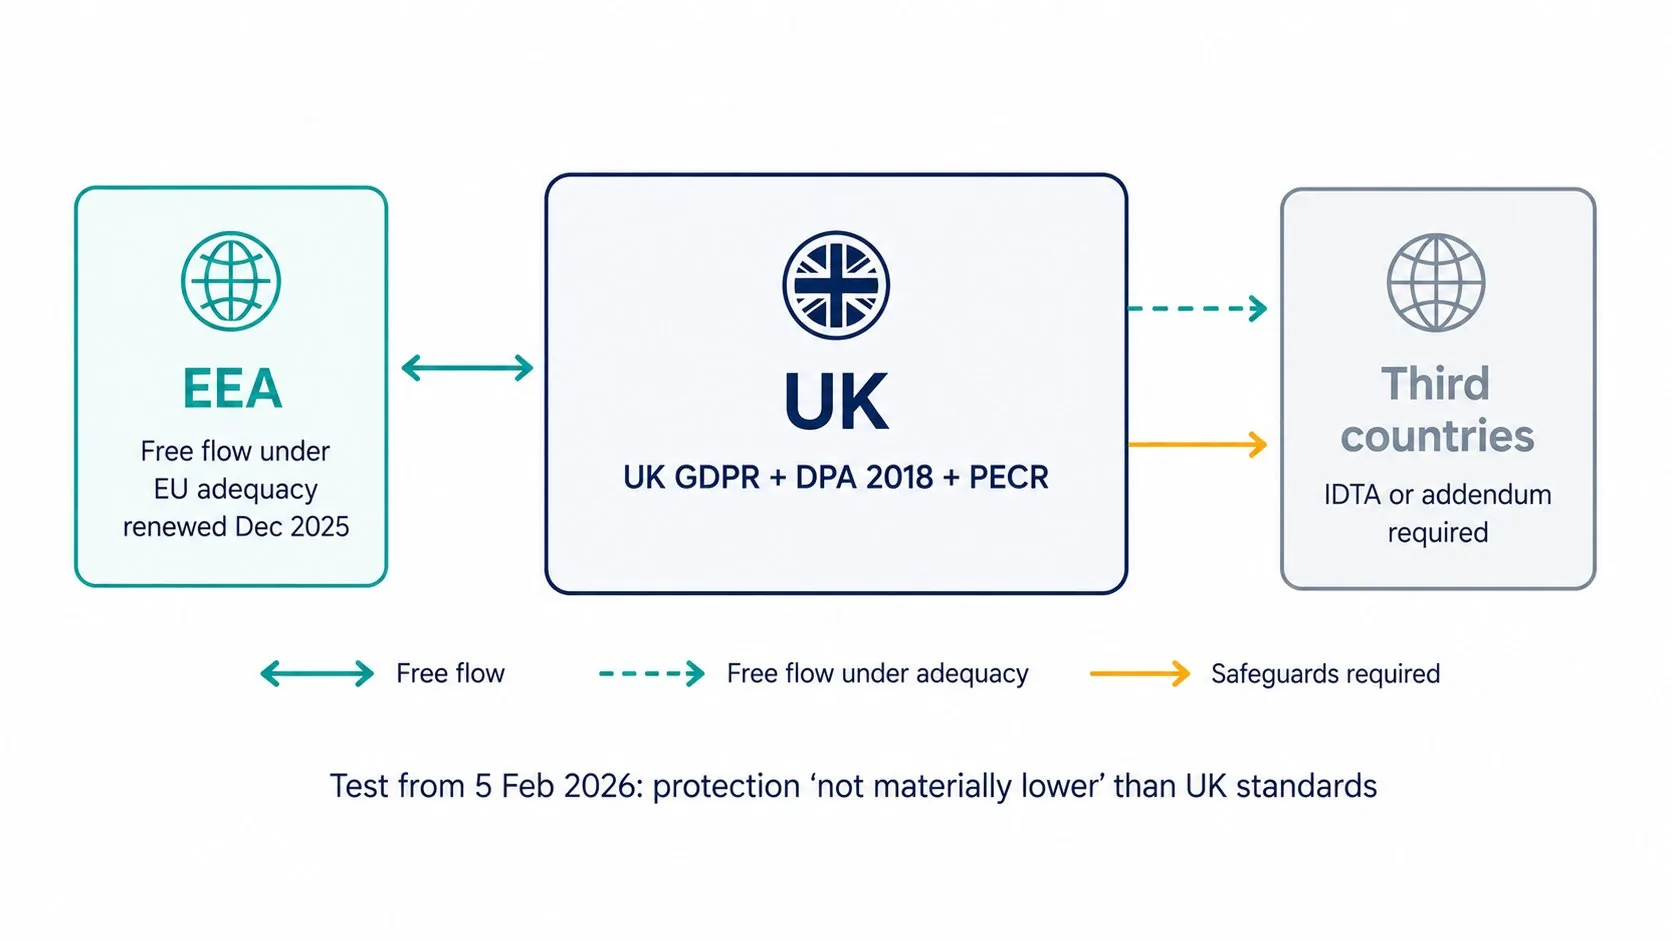
Article 3(2) extends UK GDPR to overseas organisations in two situations: when they offer goods or services to people in the UK, and when they monitor the behaviour of people in the UK.
Offering goods or services is a question of intent rather than technical reach. A website that happens to be accessible from the UK isn't necessarily within scope. Indicators of targeting include accepting payment in sterling, offering UK delivery, using the UK domain (.co.uk), providing English-language content focused on UK customers, or running marketing aimed at UK audiences. Recital 23 of the regulation sets out these signals.
Monitoring behaviour typically captures tracking, profiling, or analytics directed at UK users. A US company that tracks UK visitors' browsing behaviour through cookies, builds profiles for targeted advertising, or uses fingerprinting to understand visitor behaviour is monitoring within the meaning of Article 3(2), even if it never accepts a payment from a UK customer.
An overseas organisation within Article 3(2) normally needs a written designation of a UK representative unless an Article 27 exception applies, including the qualified occasional low-risk exception or the public-authority exception. The representative is a contact point; it is not automatically personally liable for every infringement by the represented organisation.
The household exemption
UK GDPR does not apply to processing carried out "by a natural person in the course of a purely personal or household activity". The exemption sits in Article 2(2)(c) and is sometimes shorthanded as the "household exemption".
The exemption covers genuinely personal use: a private address book, family photos, a personal diary, a list of birthdays. It also covers domestic CCTV that records only the homeowner's own property.
The exemption is narrow and fact-specific. It falls away as soon as the processing has a professional or commercial purpose, or as soon as it goes beyond the strictly domestic context. A few examples that don't qualify:
- A homeowner's CCTV that captures the neighbour's garden or the public street, as confirmed in Fairhurst v Woodard (Oxford County Court, 2021).
- A personal social media account that publishes other people's photos or information to a wide audience.
- A community group's membership processing carried out for organisational purposes rather than a natural person's purely household activity; the paper-versus-digital medium alone does not decide the exemption.
- Any processing connected to a side business, even if small or unincorporated.
For homeowners with cameras, see our CCTV guide for the detailed application of the household exemption.
Small businesses, charities, and sole traders
There is no GDPR exemption for small businesses, charities, or sole traders. All three are within scope as soon as they process personal data, which is essentially as soon as they have a customer list, employees, donors, or a website that collects information.
What does scale with size is how the regulation applies. Several specific obligations carry narrow exemptions or proportionality:
- Processing records — organisations with fewer than 250 employees must document activities that are non-occasional, likely to pose a risk, or involve special category or criminal offence data. Other qualifying activities can still benefit from the exception.
- DPO appointment — required for public authorities or bodies, subject to the judicial exception, and where core activities involve large-scale regular and systematic monitoring or large-scale special category or criminal offence data processing.
- Data protection impact assessments — only required for high-risk processing.
Core duties still apply to processing within scope. Rights responses are normally due within one calendar month, with defined adjustments and extensions. Reportable breaches require notification without undue delay and, where feasible, within 72 hours of awareness.
Charities are within scope. Fundraising activity, donor management, beneficiary records, and supporter communications all involve personal data and all attract GDPR obligations. The ICO has issued guidance specifically for the charity sector and has taken enforcement action against charities — for example the £7,500 fine against Central YMCA in 2024 over a data breach that exposed the email addresses of people on an HIV support programme.
Sole traders are within scope. A self-employed plumber holding customer contact details on a phone is a controller of personal data. They need a lawful basis, they need to be transparent, and they need to be able to respond to subject access requests. The data protection fee — paid to the ICO — applies unless an exemption is available.
The ICO and its enforcement role
The ICO regulates UK data protection law, including UK GDPR, the Data Protection Act 2018 and PECR. Its tools include guidance, complaints handling, investigations, notices, reprimands, audits, fines and prosecution of specific offences.
The DUAA changed the regulator's governance. On 30 September 2026 it transitioned from the single-Commissioner model to the Information Commission, overseen by a collective board. Its core regulatory responsibilities continue.
Enforcement can include financial penalties and other measures in both the public and private sectors. The outcome depends on the legal powers and circumstances; it is incorrect to say that the four largest UK penalties all occurred in 2025. British Airways and Marriott received £20 million and £18.4 million penalties in 2020.
For the full picture of enforcement trends and fine sizes, see our GDPR fines guide.
How to check if GDPR applies to you
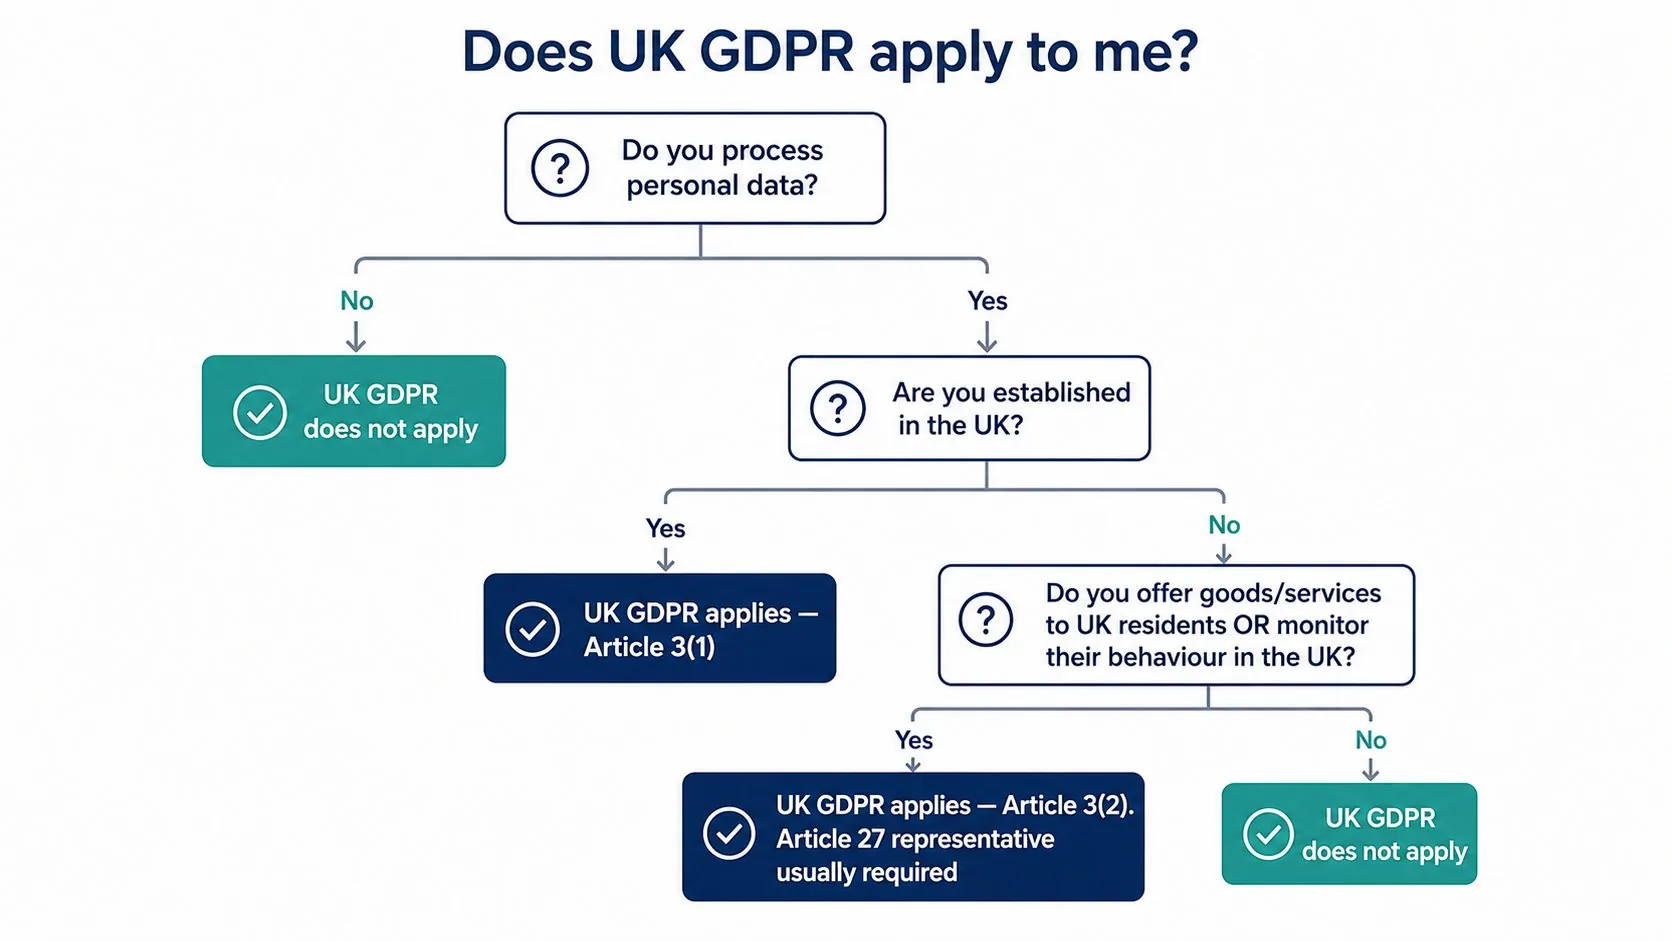
A practical sequence:
- Do you process information relating to identifiable living people? Names, contact details, online identifiers and images can be personal data depending on the context. Consider automated processing and structured manual records. See our personal data guide for detail.
- Does the processing fall within Article 3? This includes processing in the context of a UK establishment, or relevant overseas processing linked to offering goods or services to people in the UK or monitoring their behaviour there. The test is not simply whether the person is a UK resident.
- Is the processing purely personal or household? If yes, the household exemption applies. If the processing has any commercial, professional, or wider-than-household purpose, the exemption is lost.
- Identify your role for each activity from the actual purposes and means. Controllers and processors have different responsibilities, and an organisation can have both roles for different activities. See our controller and processor guide.
- Have you paid the ICO's data protection fee? Most UK controllers must pay an annual fee to the ICO unless an exemption applies. The amount depends on the size of the organisation. Failure to pay is itself an enforcement risk separate from GDPR compliance.
If you're in scope, the next step is understanding what UK GDPR actually requires of you. Our hub guide and seven principles guide are the starting points.
Frequently asked questions
Does GDPR apply to small businesses?
Yes, there is no general size exemption. Specific duties have their own thresholds and exceptions, including Article 30's activity-specific exception for some processing by organisations with fewer than 250 employees.
Does GDPR apply to charities?
Yes. Charities process personal data (donors, beneficiaries, supporters, volunteers) and are within scope. The ICO has taken enforcement action against charities, including a £7,500 fine against Central YMCA in 2024.
Does GDPR apply to sole traders?
A sole trader processing personal information for their business can be a controller and must comply with the relevant duties. Check the fee assessment separately: an exemption from the ICO fee is not an exemption from data protection law.
Does GDPR apply to US companies with UK customers?
Yes, if the US company offers goods or services to people in the UK, or monitors their behaviour. The company is within UK GDPR scope under Article 3(2) and must usually appoint a UK representative under Article 27.
Who enforces GDPR in the UK?
The Information Commission, which continues to use the ICO name. It formally replaced the single-Commissioner structure on 30 September 2026.
Is GDPR the same as the Data Protection Act?
No, but the two work together. UK GDPR provides the core rules; the Data Protection Act 2018 supplements them with UK-specific provisions and exemptions. They are separate pieces of legislation.
Related guides
- Data controller vs data processor: what's the difference?
- GDPR cookie consent in the UK: rules after the DUAA 2025
- GDPR data breach: what to do in the first 72 hours
Make sure everyone who handles personal data in your organisation is trained to do it safely and lawfully.
Explore the GDPR & Data Protection Course →Sources & references
- UK GDPR Article 2: material scope
- UK GDPR Article 3: territorial scope
- UK GDPR Article 27: representatives and exceptions
- ICO: processing records and small organisations
- ICO: Information Commission transition
- ICO: Central YMCA enforcement,2024
- ICO: Annual Report 2020/21
Mark writes about data protection, GDPR compliance and accredited online training for GDPR & Data Protection Course, part of Online CPD Academy.