A practical guide to privacy notices under UK GDPR — what Articles 13 and 14 require, the difference between Article 13 and Article 14 information, layered notices, and a template structure UK organisations can adapt.
Privacy information explains what an organisation does with personal data and helps deliver the right to be informed. It is part of demonstrating transparent processing, alongside the organisation's actual practices and other accountability records.
Getting it wrong is one of the most visible compliance failures. A privacy notice that is hard to find, written in dense legalese, or missing the items Articles 13 and 14 require is a breach by itself, and a sign that the underlying processing has not been thought through.
This guide covers what the privacy notice must contain, the difference between data collected directly and data obtained elsewhere, the layered approach the ICO expects on modern websites, and a template structure you can adapt.
Privacy notice vs privacy policy
The two terms are used interchangeably in UK practice, and there is no legal distinction. UK GDPR uses neither phrase — it talks about “information to be provided” under Articles 13 and 14. The ICO’s preferred term is “privacy information” or “privacy notice”.
Websites use both labels. What matters is that people receive clear, accessible information about the actual processing and the required content, rather than the name given to the document.
An internal data protection policy sets expectations for staff, while an outward-facing privacy notice informs individuals. An organisation may need both; one does not substitute for the other.
What Article 13 requires
Article 13 applies when personal data is collected directly from the individual. The notice must be provided at the point of collection — in the form, on the page, during the call. Article 13(1) and 13(2) together list the required content:
- The identity and contact details of the controller — and, where applicable, of the controller’s representative and any Data Protection Officer.
- The purposes of the processing and the lawful basis for each purpose. Where legitimate interests is the basis, the specific legitimate interests pursued.
- The recipients or categories of recipients of the personal data, including any processors.
- Relevant international transfers, the existence or absence of an adequacy decision, and the applicable safeguards and how to obtain a copy or access them. UK transfer safeguards may include the IDTA or the UK Addendum to EU Standard Contractual Clauses.
- How long the personal data will be stored, or the criteria used to determine that period.
- The individual’s rights — access, rectification, erasure, restriction, portability, objection, and the rights related to automated decision-making.
- The right to withdraw consent at any time, where consent is the basis for processing.
- The right to complain to the ICO.
- Whether providing the personal data is a statutory or contractual requirement, and what happens if the individual does not provide it.
- Qualifying significant solely automated decision-making, with meaningful information about the logic, significance and envisaged consequences as required by the current provisions.
The notice has to be in clear and plain language. The ICO has been explicit that dense legalese, jargon, and burying important terms in long paragraphs do not satisfy the transparency principle, even where the content technically appears.
Article 12 permits standardised icons alongside privacy information to help present an understandable overview. Icons are optional and do not replace the required information.
What Article 14 requires
Article 14 applies when personal data is obtained from somewhere other than the individual — bought from a list provider, scraped from a public source, received from a partner organisation, generated by another controller and shared.
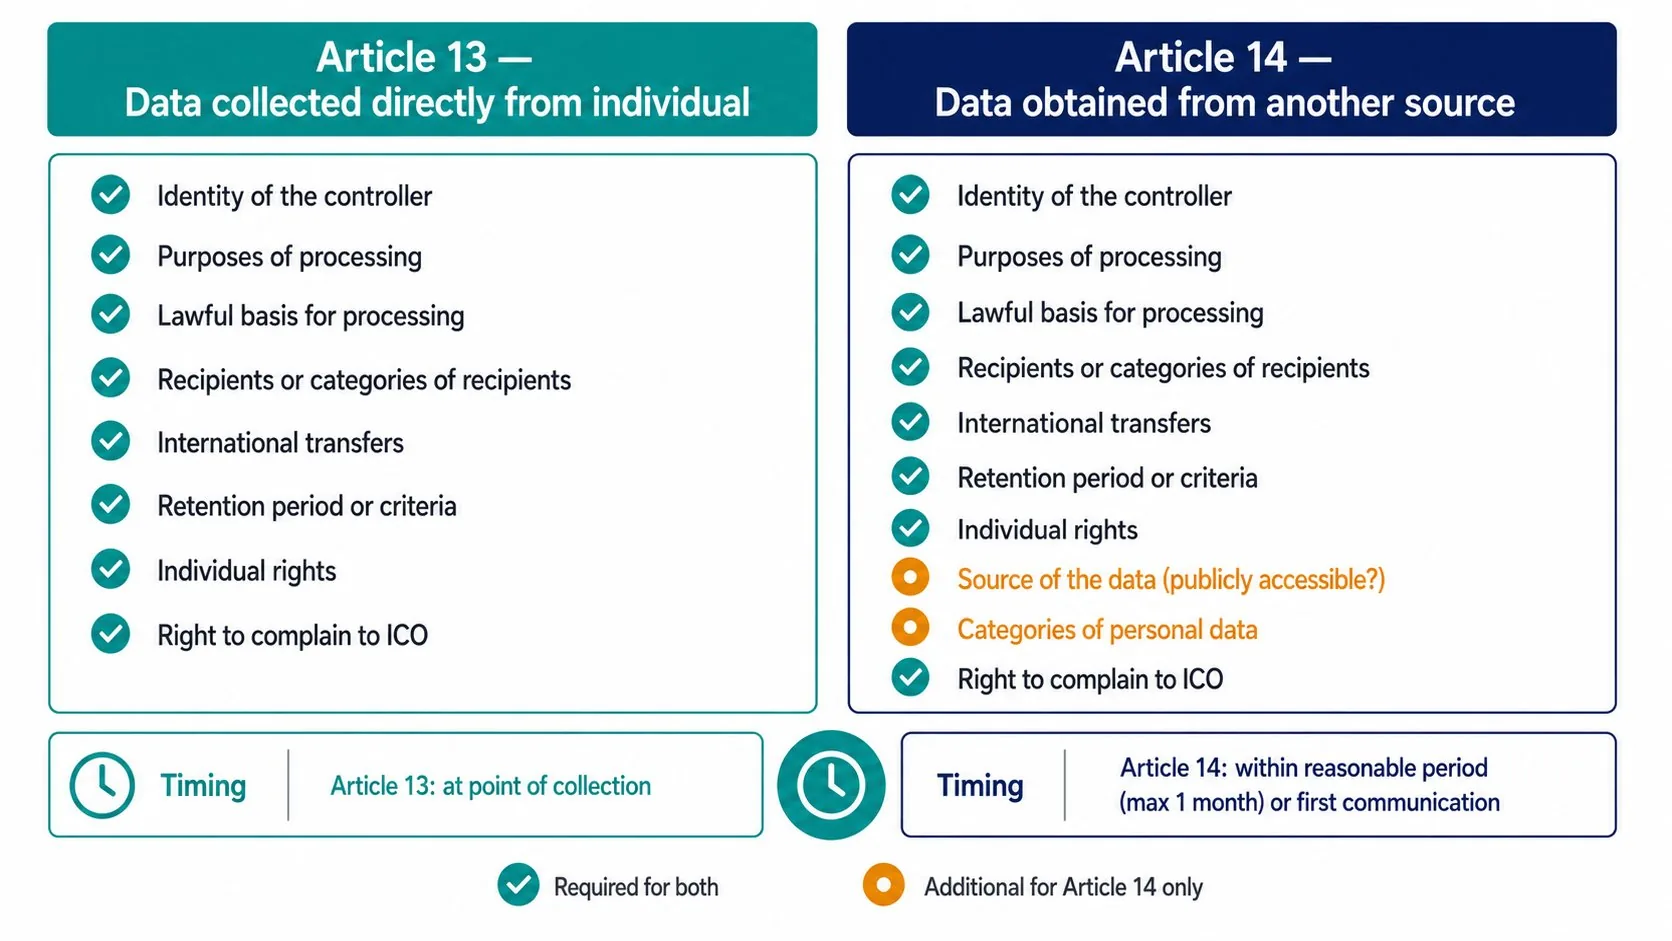
Article 14 overlaps substantially with Article 13, but the information requirements are not identical. In particular:
- The categories of personal data involved (because the individual cannot see what was collected).
- The source of the personal data, including whether the source was publicly accessible.
- Article 13's statement about a statutory or contractual requirement to provide information is not a separate Article 14 requirement. Tailor the notice to how the information was obtained.
Timing is also different. The information must be provided within a reasonable period after obtaining the data — and in any event within one month. If the data will be used to communicate with the individual, the notice must be provided at the latest at the time of the first communication. If the data will be disclosed to another recipient, the notice must be provided at the latest when the disclosure occurs.
Article 14(5) sets out exemptions. Notice does not need to be provided where:
- The individual already has the information.
- Providing the information would be impossible or involve disproportionate effort, or would be likely to prevent or seriously impair protected archiving, research or statistical objectives, where the relevant conditions and safeguards are met.
- Obtaining or disclosing the data is required by UK law that provides appropriate safeguards.
- The data is subject to a duty of professional secrecy.
The DUAA amended the transparency rules for research and related purposes, including a qualified exemption when previously collected information is reused. These provisions require a documented assessment and safeguards; impracticality alone is not a general exemption from informing people.
Layered notices and just-in-time notices
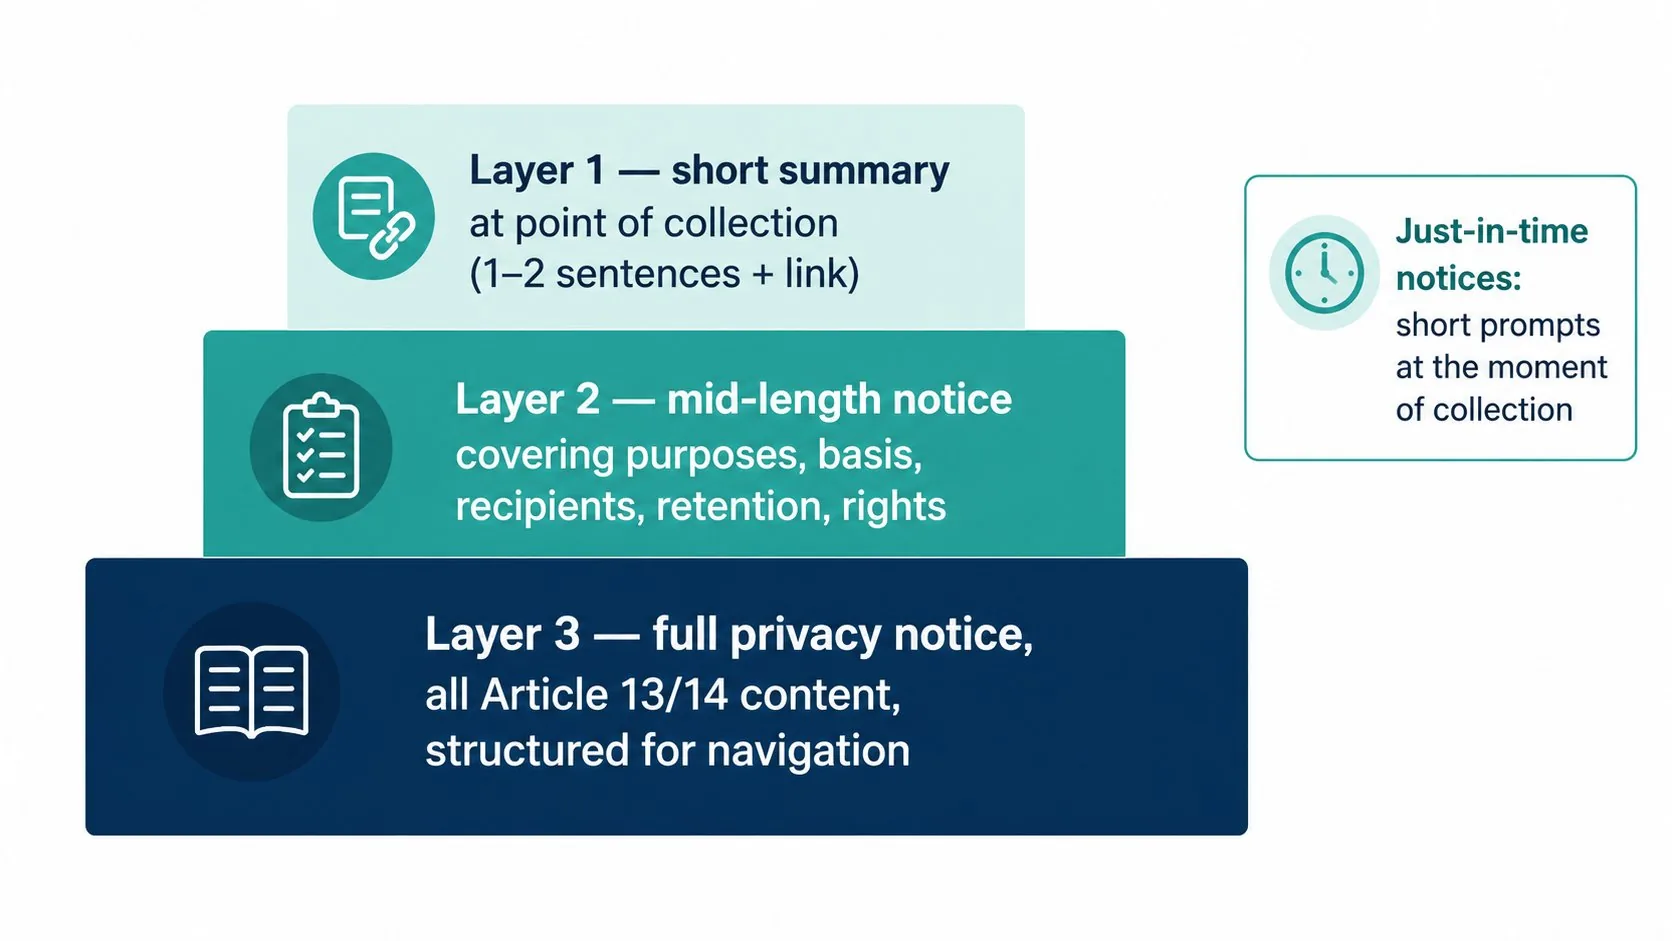
A layered approach can make a detailed notice easier to use. Provide key information prominently at collection and make the remaining detail readily accessible. UK GDPR does not require every organisation to use exactly three layers.
A layered notice presents privacy information in tiers:
- Layer 1 — a short, plain-language summary at the point of collection. Typically a sentence or two: “We will use your email to confirm your order. Read our privacy notice for the full picture.” A link takes the user to the next layer.
- Layer 2 — a mid-length notice that covers the main points: purposes, lawful basis, recipients, retention, rights, and the link to the full notice.
- Layer 3 — the full privacy notice with all Article 13/14 content, structured for navigation rather than narrative.
Each layer must be honest. A misleading Layer 1 doesn’t become acceptable just because the full picture sits at Layer 3.
A related pattern is the just-in-time notice: a short prompt that appears at the moment a specific piece of information is collected, explaining only what’s relevant to that field. A “why we ask for your phone number” tooltip next to the phone field is a just-in-time notice. They work well alongside a layered approach.
When to provide privacy information
Provide Article 13 information when the information is collected. A clear, accessible link beside a form can form part of a layered approach, with important or unexpected processing highlighted directly where needed.
For Article 14 data, the notice must be provided within a reasonable period and at most one month after the data is obtained — or at the first communication with the individual, if earlier. Where the data is shared with a third party as part of the original processing, the notice should be provided no later than the first disclosure.
Review privacy information when processing changes. Explain a new purpose before using information for it, and actively bring material changes to people's attention where needed for fair and transparent processing. A silently edited page may be insufficient.
Common privacy notice mistakes
Check for issues such as:
- Burying the lawful basis. The notice must state the basis for each purpose. Vague language like “we may rely on legitimate interests” without naming the specific interest does not meet the standard.
- Vague statements about possible sharing. Explain what sharing actually occurs or is reasonably envisaged, its purposes and recipients or recipient categories, so people can understand the processing.
- Missing retention periods. Article 13(2)(a) requires the retention period or the criteria used to determine it. “We will keep your data for as long as necessary” is not enough. “We keep customer order records for six years to meet HMRC retention requirements” is.
- Missing transfer information. Assess the actual data flows and entities involved, including overseas access. An international provider's name alone does not determine the transfer analysis; disclose relevant transfers and the mechanism relied on.
- Listing “rights” with no information about how to exercise them. The right to complain to the ICO needs a route — usually a link or an email address.
- Cookie-only “privacy policies”. A cookie banner is not a privacy notice. The two documents overlap but cover different things. See our cookie consent guide.
- Outdated legal descriptions. Review references to lawful bases, automated decisions and complaints against the amended law. A notice should describe the bases and rights relevant to the processing, rather than merely list every available basis.
A template structure you can adapt
A workable structure for an Article 13 notice on a UK business website:
- Who we are. The controller's identity and contact details, and representative and DPO details where applicable. A registration number can be useful but is not itself a universal Article 13 field.
- The personal data we collect. Categories — contact details, transaction information, technical information, etc. — with a brief description of each.
- How we use your personal data and our lawful basis. A table or list with one row per purpose, the lawful basis for that purpose, and (where relevant) the specific legitimate interest.
- Who we share your personal data with. Named processors or categories of recipients — payment provider, courier, hosting provider, accountant, professional advisers.
- International transfers. Destinations and safeguards.
- How long we keep your personal data. Retention period or criteria for each category, with a link to a fuller retention schedule if helpful. See our data retention guide for the principles.
- Your rights. A short summary of the eight rights under UK GDPR, with how to exercise each and the right to complain to the ICO. See our individual rights guide.
- Cookies and tracking. Brief reference and link to the dedicated cookie notice and preferences.
- Changes to this notice. A statement about how updates are made and when the notice was last reviewed.
- Contact details. A specific email or form for privacy queries.
Adapt the structure to the actual processing and the applicable Article 13 or 14 requirements. Clear headings help navigation, but accurate purposes, recipients, retention and rights are what make the information useful.
For more on where privacy notices fit alongside the wider regulation, see our hub guide to UK GDPR, our lawful basis guide, and our personal data guide.
Frequently asked questions
Is a privacy notice the same as a privacy policy?
The labels often refer to outward-facing privacy information, but an internal privacy policy may be a different document. UK GDPR requires the relevant information under Articles 13 and 14, whatever heading is used.
Who must have a privacy notice?
Controllers must provide the relevant privacy information unless an applicable exemption applies. There is no general small-business exemption. A processor does not automatically have the same direct notice duty for every activity it performs on a controller's instructions.
Can I link to my privacy notice?
Yes, and you usually should. The ICO accepts a linked notice provided the link is visible and reachable at the point of collection. Hidden footer links and pop-ups that appear only after data has been collected do not meet the standard.
How often should I update my privacy notice?
Review regularly and when processing or legal requirements change. There is no universal annual review deadline in UK GDPR. Explain new purposes before the further processing and bring material changes to people's attention as needed.
What’s a ‘just-in-time’ notice?
A short prompt that appears at the moment a specific piece of information is being collected, explaining what’s relevant to that field. They work well alongside layered notices, particularly for fields where the user might reasonably ask “why do you need this?”
Related guides
- GDPR cookie consent in the UK: rules after the DUAA 2025
- GDPR fines and penalties in the UK: how big, who pays, what counts
- GDPR data breach: what to do in the first 72 hours
Make sure everyone who handles personal data is trained to do it safely and lawfully.
Explore the GDPR & Data Protection Course →Sources & references
Mark writes about data protection, workplace compliance and accredited online training for GDPR & Data Protection Course, part of Online CPD Academy.