A clear guide to personal data under UK GDPR — what counts, what doesn't, the special category data list, and the difference between pseudonymised and anonymised data.
Personal data is the foundation concept of GDPR. The regulation only applies once personal data is involved, so getting the definition right is the first decision in any compliance question. The definition is broad, but it has edges that matter: information about deceased people falls outside it, truly anonymised data is outside it, and some categories — special category data and criminal offence data — get extra protection.
This guide covers the definition, worked examples, the special category list, the often-confused distinction between pseudonymised and anonymised data, and what changes when special category data is involved.
The GDPR definition
Article 4(1) of the UK GDPR defines personal data as "any information relating to an identified or identifiable natural person". The same article defines an identifiable natural person as someone who can be identified directly or indirectly, particularly by reference to identifiers such as a name, identification number, location data, online identifier, or factors specific to the physical, physiological, genetic, mental, economic, cultural, or social identity of that person.
Three elements of the definition matter:
"Any information" is deliberately broad. The information can be objective (date of birth) or subjective (a customer service note saying someone seemed agitated). It can be in any format: text, numbers, images, audio, video.
"Relating to" means the information is about the person, or used in a way that affects them. A receptionist's diary entry naming who visited and when relates to the visitors. A traffic camera image relates to the people captured in it.
An identifiable person can be identified directly or indirectly. Consider the information itself, other information available, and means reasonably likely to be used by you or another person, taking account of factors such as time, cost and available technology.
A code or identifier may be personal data even without a name attached. Assess whether it enables someone to be singled out or linked to identifying information using means reasonably likely to be available in the relevant context.
Examples of personal data
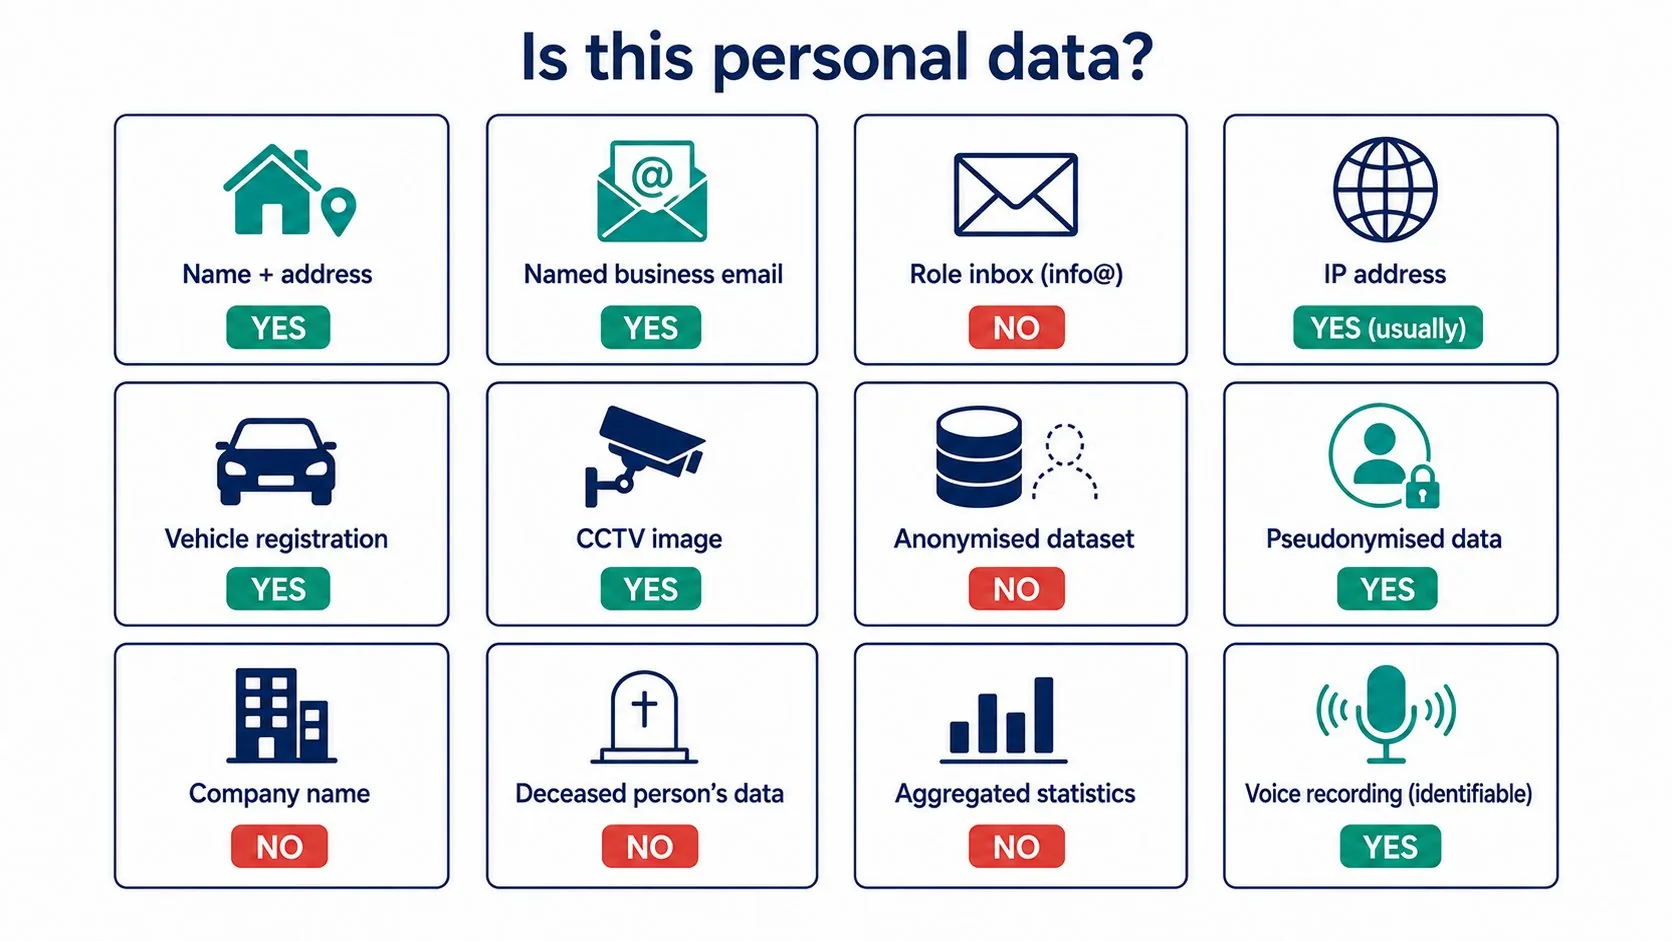
A non-exhaustive list of common categories, with notes on edge cases:
Clearly personal data
Names, addresses, email addresses, phone numbers, dates of birth, national insurance numbers, payroll numbers, employee ID numbers, photographs of individuals, voice recordings of identifiable people, CCTV footage, signatures.
Online identifiers
IP addresses, cookie identifiers, device IDs, advertising IDs, session tokens and MAC addresses can be personal data where they relate to an identified or identifiable person. The context and realistic means of identification matter; an identifier should not simply be assumed anonymous.
Location data
GPS coordinates, mobile cell tower data, address fields, and check-in records when associated with an identifiable person.
Financial and commercial information
Bank account numbers, credit card numbers, transaction histories, loyalty programme records, purchase histories, customer reference numbers.
Employment data
Salaries, performance reviews, sickness records, training history, disciplinary records, employee notes.
Vehicle registration plates
A registration plate can be personal data where it relates to an identifiable individual, including where it can be linked to keeper or other information. ANPR operators must assess their processing accordingly; not every plate identifies the driver or a natural person on its own.
Customer reference numbers and pseudonymised identifiers
Personal data when the controller (or a sub-processor) can link them back to a person.
Business contact details
This is the most-asked edge case. A generic email address (info@company.com) is not usually personal data because it doesn't identify a specific individual. A named business email address (sam.smith@company.com) is personal data — it identifies Sam Smith. The same applies to LinkedIn profiles, business mobile numbers, and named contact entries in CRM systems.
Photographs
Photos of identifiable people are personal data. Photos of crowds where no individual is identifiable usually aren't — but a sharp image of a small group typically is.
What is NOT personal data
A few important exclusions.
Information about deceased people
Data protection law does not apply after someone has died. (Note: some confidentiality duties, professional rules, and bereavement-related obligations may still apply through other legal regimes, but UK GDPR is not in scope.)
Information about companies and other legal persons
A company name, registered office, or VAT number is not personal data — companies are not "natural persons". The named director or contact person inside the company is a natural person, so information about them is personal data.
Truly anonymised data
Information is anonymised when individuals are not identifiable by means reasonably likely to be used, considering the context and information available to you or others. Removing a name alone is not sufficient.
Information that doesn't relate to a person
Aggregated statistics and logs can fall outside UK GDPR if they do not relate to an identified or identifiable person. Small groups, detailed attributes or linkable identifiers can still allow identification.
The dividing line is the same in each case: the information is outside UK GDPR if it cannot be linked to an identifiable living person, today or with reasonable effort.
Special category data
Special category processing requires an Article 6 lawful basis and one of the ten Article 9(2) conditions. Some conditions also require a basis in UK law and a relevant Data Protection Act 2018 Schedule 1 condition, with safeguards such as an appropriate policy document where required.
The eight categories of special category data are:
- Racial or ethnic origin.
- Political opinions.
- Religious or philosophical beliefs.
- Trade union membership.
- Genetic data — information about an individual's inherited or acquired genetic characteristics.
- Biometric data used for the purpose of uniquely identifying a natural person — for example, fingerprint or facial recognition systems.
- Data concerning health — physical or mental health, including health service use.
- Data concerning a person's sex life or sexual orientation.
Biometric data is special category data when processed to uniquely identify a person. An ordinary photograph is not automatically biometric special category data, but an image can also reveal other protected information, such as health or racial or ethnic origin. Assess how it is processed and what information is inferred; do not treat all photographs as ordinary data in every context.
The DUAA provides powers to amend aspects of the special category framework through regulations. The current Article 9 categories still apply; children's information and payment details are not automatically special category data merely because they are sensitive.
Criminal offence data
Article 10 of the UK GDPR covers personal data relating to criminal convictions and offences, or related security measures. This category is not "special category data" in the strict sense, but it is subject to similar restrictions. Processing is permitted only under the control of official authority or where authorised by UK law that provides appropriate safeguards.
For UK organisations, the routes for processing criminal offence data are set out in Schedule 1 of the Data Protection Act 2018. They include processing necessary for employment law purposes, for safeguarding, for legal claims, and a number of more specific situations.
Asking an applicant about criminal convictions involves criminal offence data. Identify an Article 6 lawful basis and official authority or applicable legal authorisation, normally a Schedule 1 condition, before collecting it.
Pseudonymised vs anonymised data
The two terms get used interchangeably, but they are technically and legally different — and the difference determines whether UK GDPR applies.
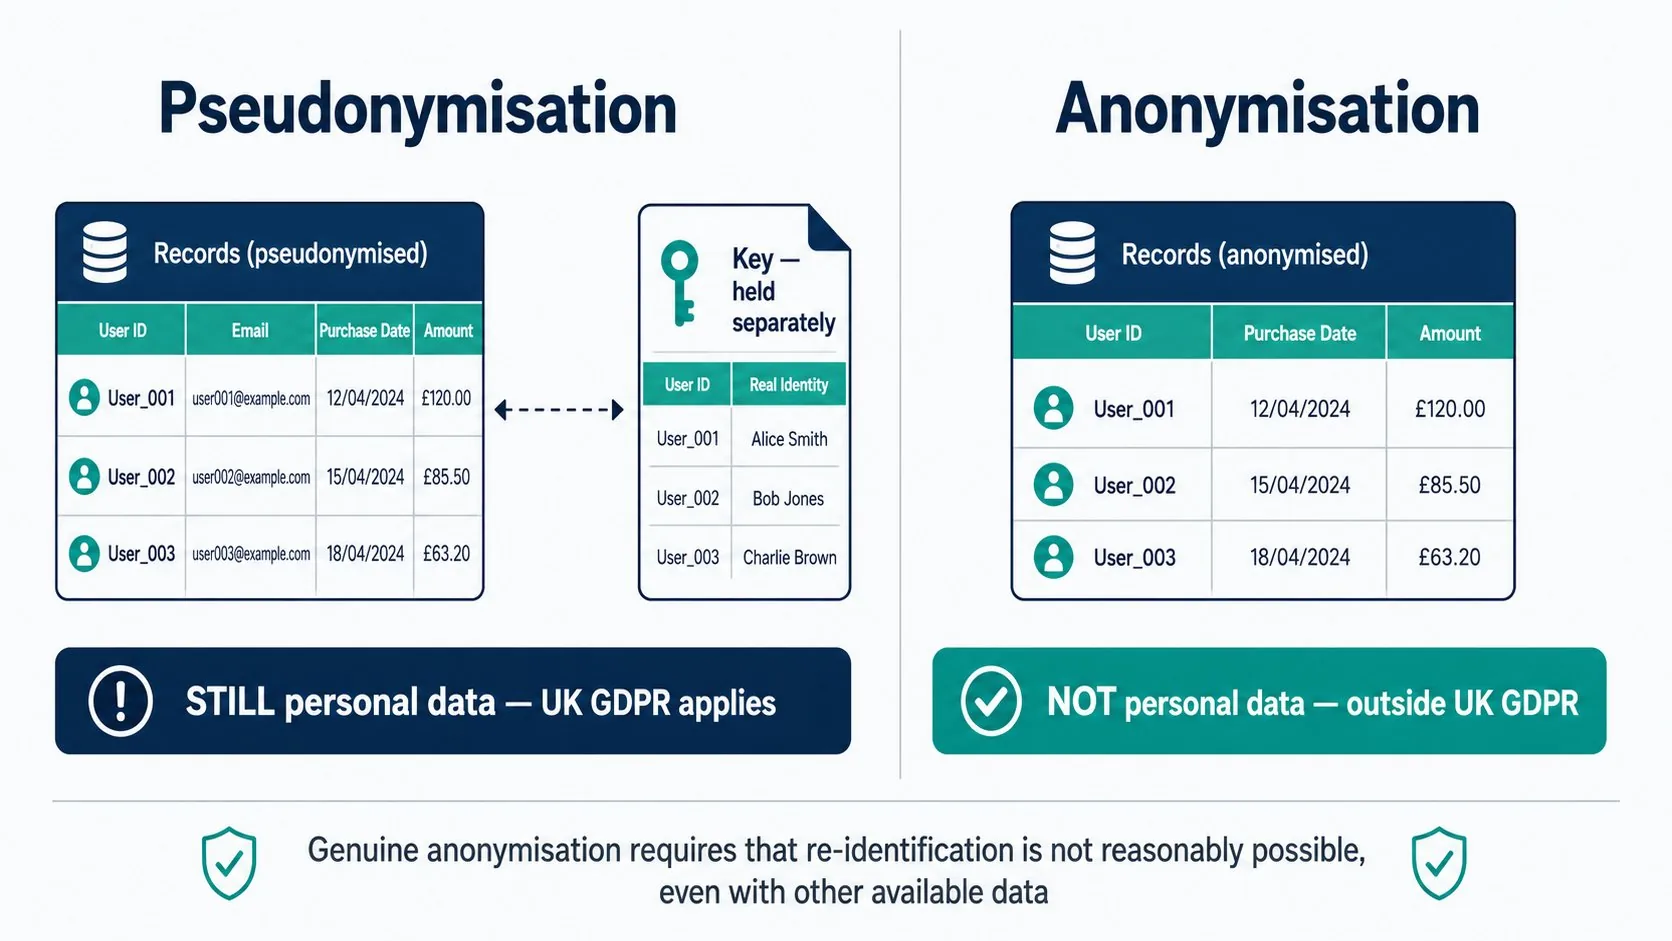
Pseudonymised data is personal data where identifying fields have been replaced with codes or tokens. The original identifiers are kept separately, typically with access controls. A customer number that maps back to a name in a separate file is pseudonymised — the link still exists, just not in the working dataset.
Pseudonymised data is still personal data. UK GDPR applies to it. Pseudonymisation is a security technique — it reduces the risk of identifying individuals in the working dataset — but it does not remove the data from the scope of the regulation.
Anonymised data is data from which a person cannot be identified, even with reasonable effort and even when combined with other available information. There is no link back to the individual. Anonymised data is outside UK GDPR.
The standard for genuine anonymisation is high. Simply removing names is not anonymisation. Removing names and other direct identifiers is often not anonymisation either — the remaining attributes can re-identify people in many real-world datasets. The ICO and the EU's data protection authorities have published guidance on what counts; the practical takeaway is that anonymisation requires assessment, not just a few field deletions.
If you anonymise data, document the process. You will need to demonstrate that re-identification is not reasonably possible, and the burden of proof sits with you.
How this changes your compliance duties
Once you know what personal data you process — and what subset is special category or criminal offence data — your obligations under UK GDPR follow:
- Identify an Article 6 lawful basis for each processing activity. Special category data also needs an Article 9 condition and, where required, a Schedule 1 condition. Criminal offence data requires official authority or an applicable legal authorisation and safeguards.
- You need a privacy notice under Articles 13 and 14 covering what data you process and why.
- You need to enable individuals to exercise their rights, which depend on what categories of data you hold.
- You need to apply the principles — particularly data minimisation (collect only what you need) and storage limitation (keep it only as long as necessary).
- You need to apply appropriate security under Article 32, with extra care for special category and criminal offence data.
For more on each of these, see our seven principles guide, lawful basis guide, and individual rights guide.
Frequently asked questions
Is an IP address personal data?
An IP address can be personal data if it relates to an identifiable individual, including when combined with logs or other reasonably available information. Its status depends on the processing context and realistic means of identification.
Is a business email address personal data?
A generic role-based address (info@, sales@) is generally not personal data — it doesn't identify a specific person. A named address (firstname.lastname@company.com) is personal data because it identifies the individual.
Is anonymised data personal data?
Genuinely anonymised information is outside UK GDPR where identification is not reasonably likely in the relevant context. Pseudonymisation normally leaves information as personal data because additional information can still link it to a person.
What is special category data?
A defined set of more sensitive personal data: racial or ethnic origin, political opinions, religious or philosophical beliefs, trade union membership, genetic data, biometric data for identification, health data, and sex life or sexual orientation.
Is health data always personal data?
Yes, when it relates to an identifiable person. Aggregated health statistics that don't trace back to an individual are not personal data, but most health records, GP notes, and occupational health files are both personal data and special category data.
Are photos personal data?
Photos that show recognisable individuals are personal data. Crowd shots where no individual is identifiable usually aren't, though the boundary depends on resolution and context.
Related guides
- GDPR cookie consent in the UK: rules after the DUAA 2025
- GDPR fines and penalties in the UK: how big, who pays, what counts
- GDPR data breach: what to do in the first 72 hours
Make sure everyone who handles personal data understands what GDPR covers and how to stay compliant.
Explore the GDPR & Data Protection Course →Sources & references
- ICO: what is personal information?
- ICO: lawful basis, special category and criminal offence data
- UK GDPR Articles 4, 9 and 10
- ICO: anonymisation and identifiability
Mark writes about data protection, GDPR compliance and accredited online training for GDPR & Data Protection Course, part of Online CPD Academy.